The cyber front never sleeps, Digital Defenders |
Stolen source code, active exploits, global crackdowns—from F5’s BIG-IP leak to Apache and Windows flaws. Even human overconfidence hits the threat list.
Before we jump into the news: Help define the future of industrial AI. Share your insights in our seven-minute survey for a chance to win a $100 gift card. |
|
| Here’s what you need to know: |
|
|
F5 Hit as Hackers Snatch BIG-IP Source Code |
Nation-state hackers infiltrated F5’s internal systems, stealing portions of the BIG-IP source code and details about undisclosed vulnerabilities.
The incident affected F5’s globally deployed BIG-IP platform, which is used by 48 of the Fortune 50 companies and over 23,000 customers. While no active exploitation or supply chain compromise has been found, the incident underscores how APT groups increasingly weaponize vulnerability intelligence. |
F5 has released patches for the vulnerabilities and enlisted other security firms for the investigation.
Implement zero-trust, monitor with SIEM/XDR tools, use F5 diagnostics for vulnerability management, secure the software supply chain with code-signing and testing, and regularly test incident response and recovery plans. |
Apache ActiveMQ Vulnerability Opens Door to System Takeover |
A critical flaw in Apache ActiveMQ’s NMS AMQP Client lets attackers execute code on vulnerable systems via insecure deserialization.
Affecting all versions through 2.3.0, the flaw exposes .NET client users to full system compromise via malicious AMQP brokers, enabling remote malware deployment or data theft across enterprise environments. Apache has released a patch for the vulnerability.
Apply the patch, restrict AMQP traffic to trusted networks, enforce strict input validation, monitor, harden runtime environments, and conduct audits. |
CISA Sounds Alarm on Active Windows RasMan Vulnerability |
CISA issued an emergency alert for an actively exploited Windows flaw that lets attackers escalate privileges through the Remote Access Connection Manager (RasMan) service.
Tracked as CVE-2025-59230, the flaw affects Windows 10, 11, and Server editions, allowing attackers to exploit improper access controls to gain system privileges, install malware, and move laterally across networks.
Microsoft has released a patch. Apply Microsoft’s latest patches, disable unused remote access services, enforce MFA and least privilege, and monitor for abnormal activity. |
|
|
Code Security Check: How secure is your organization’s source code? |
|
|
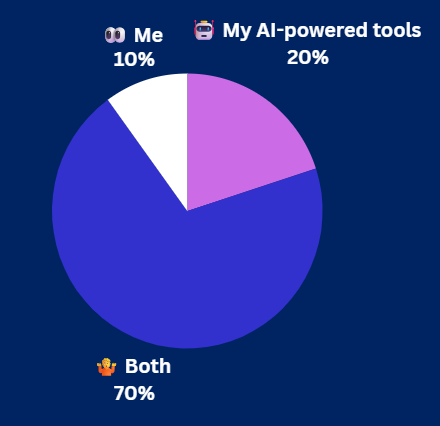
Yesterday's Pulse Check Results |
Human vs. Machine: Who spots the phish first? |
|
|
Security Tools You Can Use |
|
|
US–UK Sanctions Target Massive Cybercrime Network in Southeast Asia |
The US and UK launched their largest joint cybercrime crackdown, sanctioning 146 individuals and entities linked to Cambodia’s Prince Group TCO.
The group allegedly ran massive online scams and laundered billions through networks like Huione Group, defrauding victims worldwide via “pig butchering” schemes. |
The crackdown marks a growing global response to cyberfraud networks tied to financial crime, human trafficking, and digital exploitation.
Enhance sanctions-screening workflows, monitor for OFAC-listed entities in transaction data, and train fraud teams to identify scam patterns linked to cross-border TCO activity. |
Arctic Wolf Finds Overconfidence in Phishing Defenses Fuels Human Risk |
A new Arctic Wolf report reveals that while IT leaders remain confident in their cybersecurity posture, human error continues to drive data breaches.
Based on a survey of 1,700 IT leaders and users, Arctic Wolf’s 2025 report found 68% of organizations suffered breaches tied to phishing and risky AI use. Yet, three-quarters of leaders remain confident—even after admitting to unsafe clicks and data sharing.
The gap between perception and practice highlights a growing cultural challenge in cybersecurity leadership. Build a “human-first” security culture by pairing strong technical safeguards with continuous phishing simulations, AI-use guidelines, and positive reinforcement for incident reporting. |
|
|
Why Elastio and AWS are Your Best Defense Against Hidden Ransomware |
Malware scanners alone can’t keep up. Today’s ransomware hides in backups, evades signatures, and turns your safety net into a liability. That’s why Elastio partnered with AWS to deliver Ransomware Recovery Assurance. AWS provides unmatched scale and secure storage—but even the strongest vaults are at risk when backups are infected. Elastio adds behavior-based detection, continuous validation, and provable recovery on top of AWS snapshots and backups, ensuring you always have a clean point to restore from.
With Elastio and AWS: |
• Backups are actively monitored for ransomware that scanners miss. • Every snapshot is validated, so corruption is caught before recovery.
• Clean, audit-ready recovery paths are guaranteed for compliance and speed. |
Don’t just assume your data is safe—prove it. Together, Elastio and AWS ensure confidence that their data is both secure and resilient. |
|
|
Are You Doing Enough to Protect Your IP? |
As threat actors increasingly target source code and intellectual property (IP) to uncover vulnerabilities or steal proprietary innovations, securing development environments has become mission-critical. From supply chain attacks to insider leaks, even a minor lapse in code security can lead to major data breaches and long-term business losses.
|
How to lock down your source code: |
- Control and verify access: Enforce role-based permissions, multifactor authentication (MFA), and strict identity management to minimize insider and external risks.
-
Secure and monitor the development pipeline: Protect code with signing, encryption, and audit logging while managing secrets safely and monitoring for tampering or anomalies in real time.
-
Detect and fix vulnerabilities early: Integrate SAST, DAST, and continuous scanning tools to identify and remediate weaknesses throughout the software lifecycle.
|
Protecting source code isn’t just about compliance—it’s about preserving innovation and trust. By locking down your source code at every stage, you strengthen your organization’s defenses and help protect your software from the inside ou |
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|