The attacks aren't slowing down, Digital Defenders. |
The Pentagon is pulling back on cyber, Chrome flaws are being exposed, and AI phishing is going next-gen. |
|
|
Here’s what you need to know: |
|
|
Pentagon Slashes Cyber Training as Threats Surge |
The Department of War is cutting mandatory cybersecurity and information management training across US forces, drawing sharp criticism from cybersecurity professionals.
Aimed at reducing “distractions” and prioritizing kinetic warfare, the move comes as China, Russia, and Iran intensify cyber operations—prompting warnings that the timing couldn’t be worse amid rising military data breaches. |
The changes are directed to be “implemented expeditiously” per the memo.
Modernize training with realistic simulations, promote a no-blame reporting culture, enforce zero-trust segmentation, and strengthen detection and intelligence sharing to stay mission-ready against evolving threats. |
Chrome Exploit Triggers Emergency Patch Push |
A critical Chrome V8 vulnerability now has public exploit code, enabling full sandbox escape through WebAssembly and JS promise-integration vulnerabilities.
The PoC uses a MurmurHash64A birthday collision to induce nullability confusion, then abuses nested promise stack switching to build an ROP chain and run shellcode. This enables arbitrary code execution from crafted pages, endangering desktops, headless-Chromium servers, CI systems, and any environment that runs untrusted Wasm. Google has released a patch for the vulnerability.
Update to the latest version of Chrome, block untrusted WebAssembly, and enforce enterprise browser policies to disable Wasm execution. |
Discord Users Caught in Third-Party Data Breach |
A third-party support vendor breach exposed the personal data of some Discord users, including names, emails, and a limited number of scanned government-issued photo IDs.
Although Discord’s core systems remain secure, attackers breached its support ticketing platform in an extortion attempt, exposing contact details, billing info, and message histories from users who interacted with Customer Support or Trust & Safety. Discord is investigating the attack and notifying impacted users.
Audit third-party access regularly, enforce least-privilege controls, and ensure partners meet your organization’s data security standards to prevent similar exposures. |
|
|
Vendors are weak links—how secure are yours? |
|
|
Yesterday's Pulse Check Results |
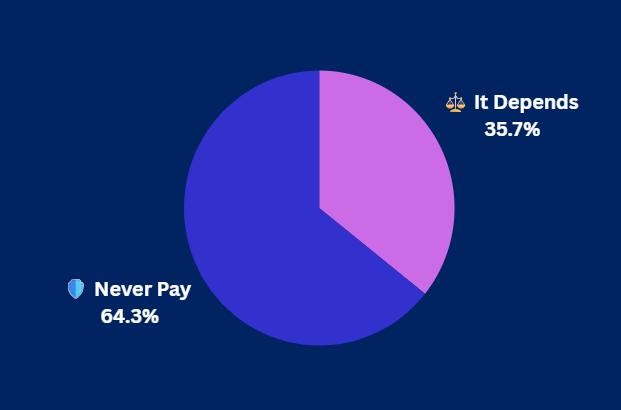
If attackers threaten to leak your data, what’s your stance? |
|
|
Security Tools You Can Use |
|
|
171K Patients Affected in Healthcare Data Leak |
Doctors Imaging Group reported a data breach that exposed the personal and medical data of over 171,000 patients.
The Florida-based provider confirmed that attackers accessed its network, stealing names, Social Security numbers, financial data, and health records. Following an investigation, the company notified authorities, informed affected patients, and pledged to implement stronger cybersecurity measures. |
Review and tighten data retention and access policies, especially around PHI, while implementing zero-trust, testing controls, and maintaining continuous monitoring. |
AI-Driven Phishing Lures Fool Users of All Ages |
AI is supercharging phishing, making scam emails nearly indistinguishable from legitimate ones—even for tech-savvy users.
A global survey found that only 46% of people could spot AI-generated phishing emails, highlighting how realistic and automated lures now exploit trust and human error to breach both personal and corporate systems. AI-powered phishing is already being seen in the wild.
Strengthen defenses by adopting phishing-resistant authentication, deploying AI threat detection, enforcing zero-trust access controls, promoting continuous training, and updating incident response plans for AI-driven threats. |
|
|
AI-driven attacks are increasing, highlighting the need for stronger identity security. Learn how Duo’s security-first IAM protects against evolving threats. |
|
|
Can You Stop a Data Leak Before It Starts? |
Data loss is costly to organizations, leading to financial penalties, operational downtime, reputational damage, and loss of customer trust.
As remote work, cloud use, and AI expand attack surfaces, safeguarding sensitive data demands proactive DLP strategies built on visibility, control, and user awareness. |
How to prevent data leaks before they happen: |
-
Protect and encrypt data: Classify sensitive files, apply DLP policies, and encrypt data in transit and at rest.
-
Monitor and control access: Use UEBA tools to detect unusual activity and restrict external sharing of cloud data to approved domains.
-
Prepare and educate: Automate encrypted backups and train employees to spot and report risky data handling.
|
Data loss prevention is about security culture as much as it is about tools. Combining automation with the human factor to reduce risk, stay compliant, and protect trust in a world where one leak can cause massive damage. |
|
|
| Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field.
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|