Big moves in the threat arena this week, Digital Defenders. |
We’re seeing $50 million ransom notes, old flaws making a comeback, delivery giants spoofed in texts, spyware hiding in “secure” apps, and a privacy clash heating up overseas. And the stakes? Higher than ever. |
|
|
Here’s what you need to know: |
|
|
Oracle Extortion: Cl0p Demands $50M After E-Business Breach |
Threat actors tied to the Cl0p group are extorting Oracle E-Business Suite customers, with ransom demands reportedly reaching $50 million. Victims were shown stolen data and file trees to pressure them into compliance, as Cl0p shifted from using zero-day exploits to credential theft and phishing. |
The group’s history of high-profile ransomware campaigns highlights its evolving tactics and global reach. Oracle is currently investigating this attack.
For impacted organizations, review and harden password reset processes, enforce multi-factor authentication across Oracle E-Business Suite accounts, and monitor for unusual login attempts. |
Grafana Flaw Exploited in Fresh Global Campaign |
Cybercriminals Impersonate FedEx, UPS, Other Brands in New Smishing Campaign |
A new smishing campaign uses “@”-stuffed URLs with brand names to dupe mobile users, Unit 42 reports. Victims are funneled to phishing or malware sites through brand-spoofed links, with attackers adding cloaking, OTP short codes, and aged domains to evade detection.
Train staff to spot smishing, enforce MFA and mobile defenses, leverage deepfake detection tools, filter and monitor URLs/logs, and conduct tabletops of IR plans. |
|
|
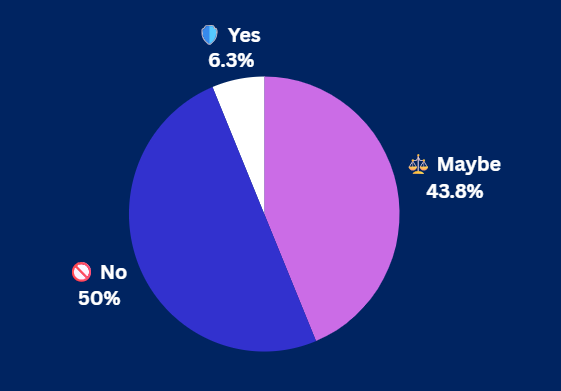
If attackers threaten to leak your data, what’s your stance? |
|
|
Yesterday's Pulse Check Results |
Do you trust US agencies to keep your threat reports safe? |
|
|
Security Tools You Can Use |
|
|
Spyware Masquerades as Secure Android Messaging Apps |
ESET researchers have identified a new spyware campaign, ProSpy and ToSpy, which leverages fake Signal and ToTok apps to target Android users in the UAE. The malware, spread through phishing and rogue stores, exfiltrates contacts, files, SMS messages, and ToTok backups, leveraging persistence and C2 to exploit trust in secure apps.
|
Security teams should enforce mobile device management controls, disable sideloading where possible, and implement an app allowlist with downloads only from authorized app stores. |
UK Renews Fight with Apple Over Encrypted Data |
The UK has renewed its clash with Apple, demanding weakened encryption under the Investigatory Powers Act.
The dispute centers on “Technical Capability Notices,” which require access to encrypted data, thereby weakening UK user security and setting a precedent that other governments may follow. A hearing has been set for early 2026. The conflict highlights the tension between digital rights and state control, signaling security teams to reassess data residency and strengthen encryption that resists government access demands. |
|
|
AI-driven attacks are increasing, highlighting the need for stronger identity security. Learn how Duo’s security-first IAM protects against evolving threats. |
|
|
Guard Against Old Vulnerabilities |
Legacy vulnerabilities are low-hanging fruit. Attackers constantly scan and exploit unpatched systems to breach organizations. Staying ahead requires discipline, visibility, and a proactive approach to patching and monitoring. |
Source: Boitumelo/Unsplash |
How to shut the door on old vulnerabilities: |
-
Patch and automate scans: Continuously update systems and automate scans to identify and remediate unpatched flaws.
- Limit exposure: Segment critical networks, enforce least privilege, and isolate legacy systems to reduce attack surfaces.
-
Monitor and stay ready: Review logs to catch exploit activity early, maintain IR playbooks, and run tabletop exercises regularly.
|
Disciplined patch management, layered defenses, and strong monitoring help reduce the risk of older vulnerabilities and stop attack chains | |
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|