Today’s headlines don’t disappoint, Digital Defenders |
From firewalls under siege to AI-powered phishing and poisoned supply chains, today’s cyber frontlines are more volatile than ever.
Every story is a reminder that attackers are innovating faster… and defenders can’t afford to stand still. |
|
| Here’s what you need to know: |
|
|
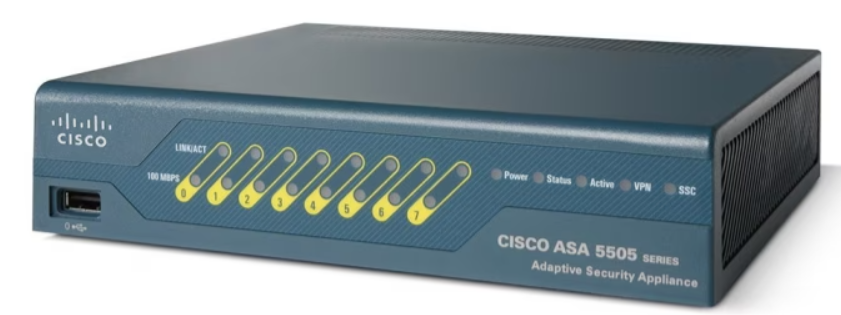
CISA Urges Patching of Cisco ASA Zero-Day Exploits |
CISA issued an Emergency Directive regarding two zero-day flaws in Cisco ASA and Firepower devices that are already under active attack.
CVE-2025-20333 and CVE-2025-20362 enable unauthenticated RCE and root-level persistence through reboots, exposing agencies and enterprises alike. Linked to ArcaneDoor, the flaws indicate state-backed actors targeting network edge infrastructure. |
These vulnerabilities are being actively exploited in the wild.
Patch immediately, run forensic checks for ROM tampering, and isolate legacy hardware. |
AI Supercharges Phishing, Proofpoint Warns CISOs |
At Proofpoint Protect 2025, executives warned that phishing is the leading global breach vector—and AI is exacerbating the problem.
Proofpoint’s Davide Canali noted that the firm scans 3.5 billion emails daily—one-third of global traffic—and that fraud drives 85% of cybercrime losses.
While AI strengthens defenses, Proofpoint warns that AI agents remain highly vulnerable to social engineering. AI-powered phishing attacks are already being seen in the wild.
Training users is no longer enough. Security teams need to invest in layered defenses, enforce phishing simulations, and scrutinize AI-driven security tools for gaps that attackers might exploit. |
GitLab Patches High-Severity DoS Vulnerabilities |
GitLab issued urgent patches for high-severity flaws, letting unauthenticated attackers crash self-managed CE and EE instances.
The most serious flaws enable DoS via crafted JSON or GraphQL queries, risking halted CI/CD pipelines, service disruption, and data loss. Other medium-severity bugs expose data and allow privilege escalation. GitLab has released a patch for the vulnerabilities. Apply the latest patches and use the skip-auto-reconfigure flag for zero-downtime updates. |
|
|
If attackers hit your CI/CD pipeline with DoS today, what happens? |
|
|
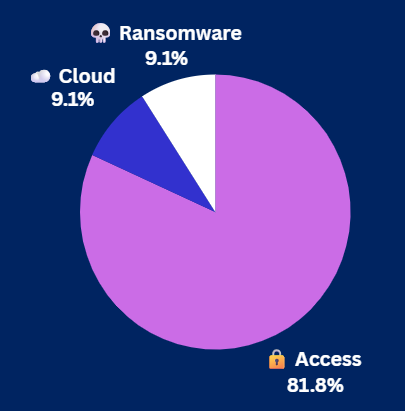
Yesterday's Pulse Check Results |
What’s your top security blind spot? |
|
|
Security Tools You Can Use |
-
Stop chasing patches: See the best vulnerability management tools that scan smarter and help you close gaps faster. Explore the top solutions.
-
Unify IT security in one dashboard: NinjaOne brings patching, backups, and endpoint protection together, eliminating complexity.
-
Ransomware recovery you can trust: AWS provides secure scale, Elastio adds detection and validation to ensure clean, uncompromised restores.
|
|
|
Fake PyPI Login Site Targets Open-Source Supply Chain |
PyPI has the registrars and CDN of the malicious domains to have them taken down.
Enforce MFA, verify domains before login, and train developers to view urgent takedown or verification notices with skepticism. |
Vietnamese Hackers Spread ‘Lone None’ Stealer via Fake Notices |
Cofense researchers have uncovered a phishing campaign by a Vietnamese group using fake copyright takedown emails to deliver malware.
Victims are lured into downloading archives disguised as legal evidence, using DLL side-loading to deploy PureLogs or the newer Lone None Stealer, which hijacks crypto wallets. The campaign uses Telegram bots for stealthy C2, with Lone None appearing in 29% of PureLogs cases since June 2025. This is an active threat in the wild.
Monitor Telegram traffic, block risky short links, and train users to spot legal-threat phishing lures. |
|
|
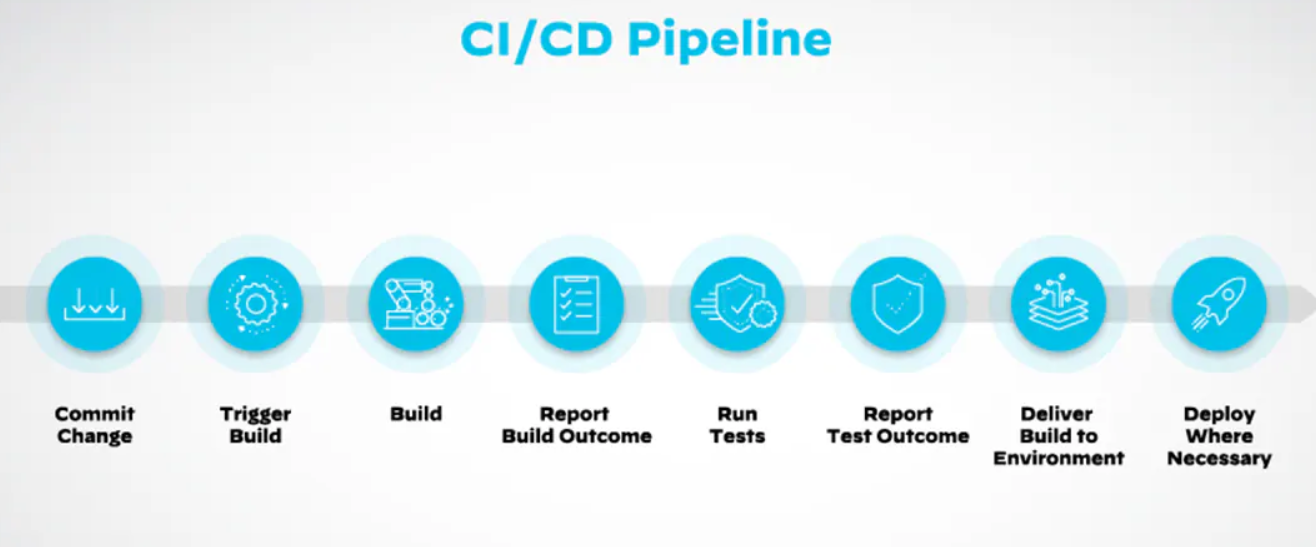
Continuous Integration and Continuous Delivery (CI/CD) pipelines are now prime targets for attackers. A single disruption or compromise can halt deployments, expose code, and leak sensitive data. With denial-of-service attacks and supply chain exploits on the rise, securing your pipeline has never been more critical. |
Source: Palo Alto Networks |
Here's how to secure your CI/CD pipelines: |
- Enforce strong access controls with MFA and least-privilege roles to limit risks from stolen or misused credentials.
- Automate code and dependency scans while isolating build environments to catch vulnerabilities and block attacker pivoting.
- Protect secrets by storing tokens and keys in secure vaults rather than scripts or configs.
- Monitor pipeline traffic for anomalies and patch CI/CD tools quickly to close high-severity flaws.
|
CI/CD pipelines power modern delivery, but they’re prime targets for downtime, data theft, and backdoored code. Strong layers of defense and continuous monitoring keep builds secure, resilient, and fast. |
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|