Some attacks wear a friendly face, Digital Defenders. |
AI browsers read hidden commands, a single bit hijacks models, and attackers slip in where you least expect. |
|
| Here’s what you need to know: |
|
|
AI Browsers Exposed: Data Theft Made Simple |
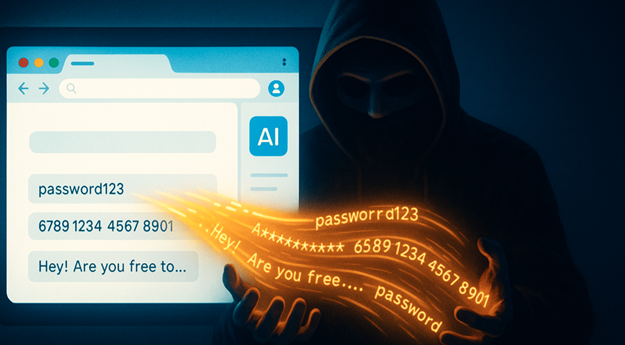
Security researchers uncovered a flaw in Perplexity’s Comet browser that shows how AI can be tricked into stealing user data. Hidden malicious instructions inside normal web content activated when users asked the AI to “summarize this page,” leading to full account hijacks, including Gmail access. |
The weakness lies in perception—AI treats every word as equally valid, even malicious ones. Any AI browser that links external data, private accounts, and outbound access is at risk—even after patches—putting consumers and enterprise systems in jeopardy. The company released a statement to CNET saying that this vulnerability has been fixed.
Until AI browsers add guardrails like sandboxing and confirmation prompts, avoid using them with high-value accounts such as banking or corporate email. |
AI Models Hijacked by a Single Bit Flip |
George Mason researchers unveiled “OneFlip,” a stealthy backdoor that hijacks neural networks by flipping a single memory bit.
Unlike data-poisoning attacks, OneFlip targets inference, remaining nearly invisible while preserving model accuracy. The technique weaponizes hardware flaws, such as Rowhammer, to stealthily alter AI behavior, achieving a 99% success rate across datasets. It poses serious risks to production systems, ranging from autonomous tools to fraud detection.
The flaw hasn’t been exploited in the wild yet, and researchers rate its practical risk as low, given the access required of an attacker. Harden AI with DRAM fault defenses, integrity checks beyond model files, and sandboxing for untrusted workloads to block inference-time backdoors. |
Git Vulnerability Opens Door to Supply Chain Attacks |
CISA issued a high-severity alert for CVE-2025-48384, a Git flaw that enables arbitrary file writes and possible code execution via mishandled carriage returns in configuration files.
The flaw, already being exploited in the wild, endangers CI/CD pipelines, builds, and developer systems by letting attackers smuggle malicious hooks with user privileges. If left unpatched, it risks supply-chain compromise and ransomware, particularly for organizations that rely on Git. Git versions starting Jul. 8, 2025, have this vulnerability fixed. Patch Git to version 2.43.7 or newer immediately. If patching isn’t possible, disable submodules or remove risky hooks from CI/CD until updates are applied. |
|
|
Git Security Check: How cautious are you with repos? |
|
|
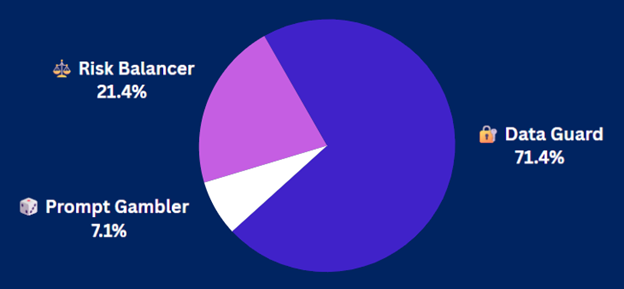
Yesterday's Pulse Check Results |
How cautious are you with prompts? |
|
|
Security Tools You Can Use |
-
Cyberattacks strike harder and faster. Discover the tools that lock down data, stop insider threats, and give you control and confidence from one simple dashboard.
-
Remote work widens your attack surface. NordLayer closes the gaps, encrypts every connection, and keeps teams secure, regardless of where they log in.
-
Geo-blocks and throttling limit you? OysterVPN unblocks streaming, shields your identity with AES-256, and secures every device on fast, zero-log servers.
|
|
|
Citrix NetScaler 0-Day Under Active Attack |
Citrix has confirmed the active exploitation of CVE-2025-7775, a remote code execution flaw in NetScaler ADC and Gateway appliances. The vulnerability stems from a memory overflow and affects multiple versions, including some still in widespread use despite being End of Life.
With no workarounds and three CVEs carrying a CVSS score of up to 9.2, unpatched Gateways, IPv6 load balancers, and hybrid deployments face risks of RCE, DoS, and lateral movement. |
Citrix has begun notifying customers and channel partners about this vulnerability and has made recommendations for upgrading vulnerable appliances.
Upgrade to fixed releases (14.1-47.48, 13.1-59.22, or later), lock management interfaces to admin networks, and audit logs for suspicious AAA, VPN, or IPv6 vserver activity. |
Massive Auchan Breach Impacts Hundreds of Thousands |
French retailer Auchan confirmed a cyberattack that compromised data from hundreds of thousands of loyalty accounts, including names, email addresses, addresses, phone numbers, and card numbers.
Though passwords and financial data were safe, the breach exposed ongoing weaknesses in retail customer databases. Attackers can weaponize stolen PII from loyalty systems in phishing, smishing, and credential-stuffing.
The company has stated that the incident has been contained, and they are notifying impacted customers. Watch for phishing tied to stolen data and strengthen defenses with Zero Trust, MFA, and SIEM monitoring. |
|
|
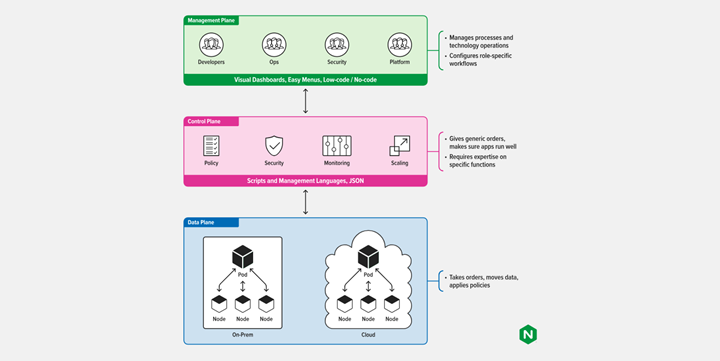
Lock the Front Door: Protect Your Management Plane |
Edge appliances, such as NetScaler, are frequent targets for attackers because their exposed management interfaces offer direct paths to privileged access. Once threat actors reach NSIP, CLIP, or SNIP addresses, they can bypass defenses, execute commands, and move deeper into your environment.
The fix? Harden your management plane before attackers find it. |
How to secure the management plane: |
- Restrict management traffic to segmented admin networks.
- Enable MFA to block stolen credentials.
- Allow connections only from trusted IPs or jump hosts.
-
Scan external assets to catch exposed management ports
- Log and alert on unauthorized access attempts.
- Patch appliances quickly to close vulnerabilities.
|
Locking down the management plane is a fast and low-cost way to prevent attackers from exploiting a single flaw and gaining full access—your front door lock against intruders. |
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|