Another day, another breach, Digital Defenders. |
If it’s connected, it’s collectible…from your Salesforce data to your car keys. Today’s cyber hit list is a reminder: every door can be a target. |
|
| Here’s what you need to know: |
|
|
Zoom, Xerox Patch Critical Windows Exploits |
Zoom and Xerox rolled out urgent patches for Windows vulnerabilities that could let attackers gain full control of affected systems. These are easy to exploit and could enable data theft or lateral movement within a corporate network. |
In Zoom’s case, an untrusted search path in multiple Windows clients could let an attacker with network access escalate privileges. This impacts Workplace, VDI, Rooms, and Meeting SDK versions earlier than 6.3.10. Xerox’s FreeFlow Core software also received a high-priority update to fix similar bugs.
Admins: apply updates immediately, lock down high-value endpoints, and monitor for unusual connections to reduce post-compromise risk. |
ShinyHunters and Scattered Spider Team Up for Salesforce Extortion |
Two of the most notorious cybercrime crews—ShinyHunters and Scattered Spider—are reportedly joining forces in a coordinated data extortion push. Investigators say the campaign leans on Scattered Spider’s playbook: high-pressure vishing calls, fake Okta login pages, and VPN-hopping for data theft.
The overlap in domain infrastructure, attack timing, and shared aliases suggests the partnership may have been active for over a year. Recent domain registrations point to a shift toward financial services targets, with banks and insurers now in the crosshairs. If your team uses Salesforce or similar cloud apps, enable phishing-resistant MFA and lock down VPN access—attackers thrive on stolen logins. |
Hyundai Offers Paid Fix for Car Lock Hacking Threat |
Hyundai is charging Ioniq 5 owners in the UK £49 ($66) for a security upgrade to block theft tools that mimic car key signals. These tools (sometimes disguised as retro Game Boys) can unlock and start targeted cars in seconds.
While this case centers on Hyundai, similar vulnerabilities affect multiple automakers, from Kia to Nissan, as criminals exploit gaps in wireless key fobs and vehicle electronics. Keyless repeaters, signal jammers, and code-grabbing gadgets are linked to roughly 40% of car thefts in England and Wales alone.
Experts say that until software and hardware defenses catch up, old-school deterrents still work: steering wheel locks, immobilizers, and guarded parking. |
|
|
How secure is your vehicle? |
|
|
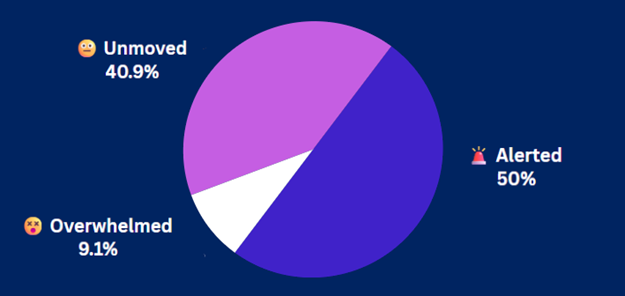
Yesterday's Pulse Check Results |
Microsoft just patched 111 flaws. What’s your reaction? |
|
|
Security Tools You Can Use |
-
Keeper Security offers secure storage, breach alerts, password sharing, and 24/7 support. Keep your digital life safe across all devices for just $3.33/month.
-
Vulnerability Management Tools help you find flaws across network and cloud environments, then prioritize and apply fixes. We found the top options to help your team choose the best fit.
-
Deploy a ready-made DNS/DHCP policy template in minutes. Save 12 drafting hours for $19 or free with TechRepublic Premium.
|
|
|
Pennsylvania AG’s Office Hit by Likely Ransomware |
Source: Commonwealth Media Services |
Security experts recently flagged exposed Citrix NetScaler devices on the office’s network as vulnerable to “Citrix Bleed 2,” a flaw exploited since May. Two devices were taken offline in late July and early August, potentially marking the breach point. Over 3,300 systems worldwide remain unpatched.
CISA has ordered federal agencies to patch immediately. The hit comes at the same time a similar cyberattack disrupted the US federal judiciary, signaling growing pressure on critical justice systems. |
FIDO Passkeys Can Be Downgraded in New Phishing Technique |
Researchers found a way to make Microsoft Entra ID’s FIDO passkeys step down to weaker logins. The attack spoofs an unsupported browser (like Safari on Windows), so Entra throws an error and prompts the user to pick a fallback (often a less secure MFA code).
Once the victim takes the bait, the attacker’s Evilginx phishing kit grabs both the credentials and the live session cookie. This lets them hijack the account without another login challenge. Experts warn this is a prime target for advanced hackers and state-backed groups as FIDO adoption grows. It’s a reminder that even phishing-resistant security can still be socially engineered into holding the door open. |
|
|
Stop Hackers From Reading Your Texts |
Encrypted messaging isn’t just personal—it’s professional. As US officials now warn, unencrypted apps leave calls and texts exposed to hackers and surveillance. |
Here’s how to lock down your conversations: |
- Choose messaging apps with end-to-end encryption like Signal, WhatsApp, or iMessage.
- Verify contacts before sharing sensitive information.
- Disable cloud backups for chats to prevent server-side exposure.
-
Keep apps updated to patch security flaws quickly.
- Avoid public Wi-Fi when discussing confidential matters.
|
|
|
|
Greg Parker is a cybersecurity and emerging tech writer who explores the intersection of digital risk, human behavior, and innovation across sensing and security technologies. |
|
|
Protect your team with premium policies, guides, and more |
Cybersecurity Insider subscribers can now get 20% off an annual subscription to TechRepublic Premium and unlock unlimited access to hundreds of customizable policy templates, step-by-step checklists, and expert-written guides. Replace days of research and drafting with proven, plug-and-play resources that help your team harden defenses and stay audit-ready — fast. Use the code CSI20 at checkout. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|