Stay informed and ready, Digital Defenders. |
A dating app has leaked thousands of private images. Google Cloud says threat intel teams are drowning in data and short on skilled analysts. Meanwhile, Russia’s largest airline has been hit by a disruptive cyberattack. |
|
| Here’s what you need to know: |
|
|
Photo ID Breach: 72,000 Images Stolen from ‘Tea’ App for Women |
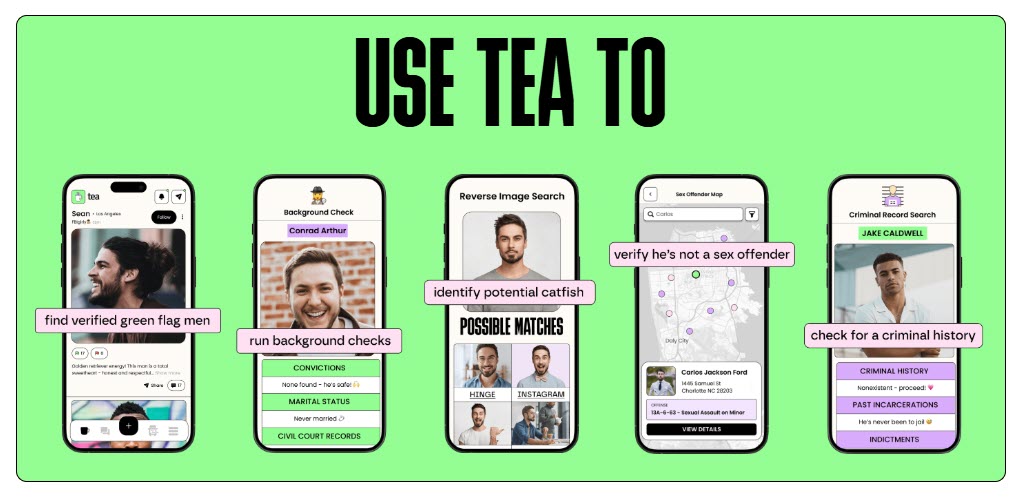
Tea, a dating app designed exclusively for women, has suffered a massive data breach, exposing approximately 72,000 selfies from a compromised "legacy data storage system.” |
Source: Tea Official Site / Screenshot |
According to the company, unauthorized access to their systems was detected on July 25. Upon investigation, they found that roughly 72,000 images—including 13,000 selfies, photo IDs submitted for account verification, and 59,000 images publicly viewable in the app—were leaked. Tea also confirmed that some direct messages were accessed during the incident.
IT Teams: Audit and upgrade legacy storage systems to modern, secure platforms to avoid similar breaches. |
Intel Overload Is Breaking Cybersecurity Teams, Says Google Cloud |
Google Cloud is sounding the alarm: threat intelligence teams are drowning in data and lack the analysts to keep up, according to the July 2025 Threat Intelligence Benchmark report by Forrester Consulting and Google Cloud. The report, based on a survey of over 1,500 IT and cybersecurity leaders, identified five key challenges: |
- Too many threat intelligence data feeds (61%).
- Lack of skilled threat analysts (60%).
- Difficulty making the data actionable (59%).
- Trouble verifying the validity and/or relevance of threats (59%).
-
Difficulty determining which intelligence applies (49%).
|
Google Cloud recommendation: Prioritize high-stakes needs and identify your adversary’s tendencies to properly allocate threat intelligence resources. |
CISA: Patch PaperCut Now or Risk Remote Code Attacks |
CISA has disclosed the active exploitation of a high-severity security flaw in PaperCut NG/MF print management software, which could allow remote code execution via cross-site request forgery attacks.
The flaw, tracked as CVE-2023-2533 with a 8.4 CVSS score, was patched in June 2023 but has now been added to CISA’s Known Exploited Vulnerabilities catalog. Vendors have until Aug. 18 to apply the necessary fixes.
If your organization uses PaperCut NG/MF (business, schools, and government agencies), update your print management software immediately to mitigate the risk. |
|
|
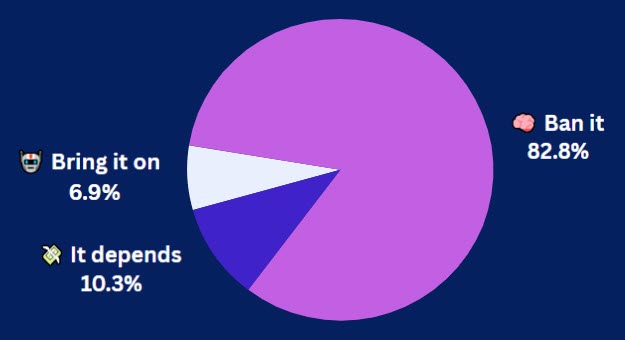
Do you trust apps to securely store your personal photos? |
|
|
Yesterday's Pulse Check Results |
How do you feel about AI setting prices? |
|
|
Security Tools You Can Use |
-
NinjaOne helps you keep tabs on every device in your environment—from mobile phones to servers—so nothing slips through the cracks.
-
TechRepublic Premium’s Antivirus Policy gives your team a clear, actionable plan to guard against threats and stay compliant.
|
|
|
One Plugin, 10K Sites, Three Dangerous Flaws |
Three security flaws in the HT Contact Form WordPress plugin have left over 10,000 sites vulnerable to remote code execution and site takeover. |
Source: Unsplash / Justin Morgan |
According to a blog post from Wordfence, two researchers reported the three vulnerabilities through its Bug Bounty Program. The flaws allow threat actors to upload or delete arbitrary files—potentially leading to RCE or unauthorized control of affected sites
Fortunately, the HasTech IT Team has already released a patch for the flaws on July 13, 2025. Site owners using HT Contact Form: Update to the latest version of the plugin immediately, to ensure your site stays protected. |
Russia’s Largest Airline Grounded Following Cyberattack |
Aeroflot, Russia’s largest airline firm, has been hit with a cyberattack that has canceled 60 flights and taken its official website offline.
Pro-Ukrainian hacker group Silent Crow has claimed responsibility for the attack, amid the ongoing Russia-Ukraine war. In a Telegram post, the group alleged that they “destroyed” Aeroflot’s systems and accessed the personal data of all Russians who have “ever flown with Aeroflot.” If you’ve recently flown with Aeroflot, consider resetting your account credentials and keeping an eye out for suspicious activity. |
|
|
Think Twice Before Installing iOS 26’s Public Beta |
Apple’s upcoming iOS 26, featuring the sleek new Liquid Glass design language, is now available as a public beta. Tempting as it may be to jump in early, you’ll want to weigh the risks before loading it onto your primary device. |
Source: Apple Newsroom / Screenshot |
Here’s why you might want to hold off: |
-
Security gaps: Early versions may include unpatched vulnerabilities that haven’t yet been discovered or patched.
- Buggy behavior: Expect crashes, app instability, and the potential loss of core functions like Bluetooth or phone calls.
- Battery drain: Beta builds often lack optimization, leading to faster battery depletion.
-
App incompatibility: Many third-party apps won’t yet be updated for iOS 26, which could lead to glitches.
|
If you’re eager to explore Liquid Glass, consider installing the beta on a secondary iPhone—not your daily driver. For most users, waiting until the official release in September is the safer (and smarter) move. |
|
|
| Senior Staff Writer at TechnologyAdvice |
Luis Millares is a seasoned tech writer with broad experience reviewing consumer gadgets and enterprise software, offering clear, reliable insights across the latest in technology. |
|
|
Protect your team with premium policies, guides, and more |
Cybersecurity Insider subscribers can now get 20% off an annual subscription to TechRepublic Premium and unlock unlimited access to hundreds of customizable policy templates, step-by-step checklists, and expert-written guides. Replace days of research and drafting with proven, plug-and-play resources that help your team harden defenses and stay audit-ready — fast. Use the code CSI20 at checkout. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|