They’re coming for you, Digital Defenders. |
Major breaches and harmful code are making the rounds. From insurance giants to gaming gear, threat actors are exploiting trust and targeting your data…and Congress is finally paying attention. |
|
|
Here’s what you need to know: |
|
|
Allianz Life Breach Hits Majority of 1.4M US Customers |
Hackers used social engineering to infiltrate a third-party cloud system tied to Allianz Life, a Minnesota-based insurance firm. |
The cybercriminals posed as trusted users to gain access and obtained personal data from most of the company’s 1.4 million US customers, financial advisors, and employees. Allianz states that its internal systems were not compromised, and the FBI was notified. Affected users will get two years of identity protection. Still, be sure to check your credit and insurance accounts for anything unusual. |
Amazon Q Developer Extension Hit by Malicious Code |
AWS confirmed that version 1.84.0 of its Amazon Q Developer extension (a tool that brings AI coding help into Visual Studio Code) was compromised by hackers.
A misconfigured GitHub token used in AWS’s automated build system let an attacker add malicious code to the extension’s public codebase. AWS quickly revoked the token, removed the bad code, and released a clean version 1.85.0. Anyone still using version 1.84.0 should delete it and install version 1.85.0 immediately, even if it came from a fork or copy. |
Lawmakers Crack Down on AI-Powered Pricing Tactics |
A new bill aims to outlaw “surveillance pricing,” where AI uses personal data to adjust prices or wages.
The FTC found that at least 250 firms use personal data, such as device type, income signals, and parenting status, to target consumers with higher prices. Delta Air Lines already applies AI-driven dynamic pricing to 3% of fares and plans to expand to 20% by year’s end, using software from Fetchr.
To avoid price manipulation, use privacy tools, clear browser data regularly, and limit sharing of personal details with retailers. |
| |
How do you feel about AI setting prices? |
|
|
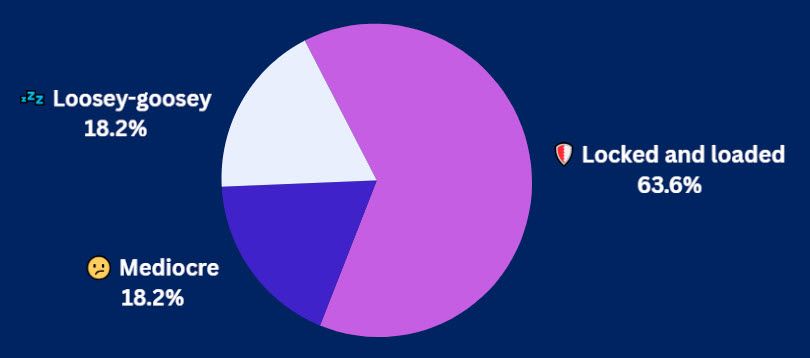
Yesterday's Pulse Check Results |
How tight is your anti-malware game? |
|
|
Security Tools You Can Use |
-
Vulnerability Management Tools help you find flaws across network and cloud environments, then prioritize and apply fixes. We've identified the top options to help your team select the best fit.
-
Keeper is a top-rated password manager with end-to-end encryption, dark web monitoring, and secure file storage across unlimited devices—now 30% off all one-year plans.
-
IT Career Certification Pathway Bundle gives you lifetime access to eight expert-led courses and 169 hours of training to launch or grow your IT career—now just $34.99 (80% off).
|
|
|
Android Malware Impersonates Banking Apps to Steal Data |
Researchers uncovered a sophisticated Android malware campaign using fake Indian bank apps to steal credentials, debit card info, SMS messages, and call data. |
The malware abuses Android permissions, hides itself from users, and uses Firebase as a command-and-control server to quietly exfiltrate data. Attackers spread the apps through phishing texts, fake websites, QR codes, and trojanized utility apps. Avoid installing apps from untrusted sources, and stick to Google Play or verified developers whenever possible. Always check app reviews, permissions, and publisher reputation. |
Gaming Mouse from Endgame Gear Linked to Malware-Infected Software |
Endgame Gear revealed that its configuration tool for the OP1w 4k v2 gaming mouse was compromised with malware and distributed via its product page between June 26 and July 9.
The issue was isolated to that page, with all other official sources, including the main downloads site and GitHub, remaining unaffected. Always download gaming software from verified sources, and run antivirus scans if you suspect tampering or unusual system behavior. |
|
|
Treat Gaming Gear Like Any Other Attack Vector |
Gaming devices, such as mice, keyboards, and headsets, often require deep system access…and hackers are aware of this. Bundled software and drivers can hide malware, escalate privileges, or open backdoors just like any endpoint. |
Here’s how to keep your setup secure: |
-
Download only from official sources: Use trusted vendor sites for firmware and drivers.
- Scan before you install: Run antivirus checks on all gaming software installers.
- Avoid kernel-level tools: Don’t use software that needs deep system access unless absolutely necessary.
-
Verify integrity: Look for digital signatures or checksums before installing updates.
- Update regularly: Keep peripheral firmware current using official software channels.
|
Gaming gear may look harmless, but the software behind it can open real doors for attackers. Treat it like any other endpoint. |
|
|
|
Greg Parker is a cybersecurity and emerging tech writer who explores the intersection of digital risk, human behavior, and innovation across sensing and security technologies. |
|
|
Protect your team with premium policies, guides, and more |
Cybersecurity Insider subscribers can now get 20% off an annual subscription to TechRepublic Premium and unlock unlimited access to hundreds of customizable policy templates, step-by-step checklists, and expert-written guides. Replace days of research and drafting with proven, plug-and-play resources that help your team harden defenses and stay audit-ready — fast. Use the code CSI20 at checkout. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|