Watch out, Digital Defenders! 🛡️ |
Threats are escalating fast—Google’s OSS Rebuild tackles supply chain tampering, while active SharePoint exploits demand urgent patches. Meanwhile, new malware tricks Windows features to steal crypto creds. Get in the know and patch quickly. |
|
| Here’s what you need to know: |
|
|
Google Unveils OSS Rebuild to Detect Tampering in Popular Open-Source Packages
|
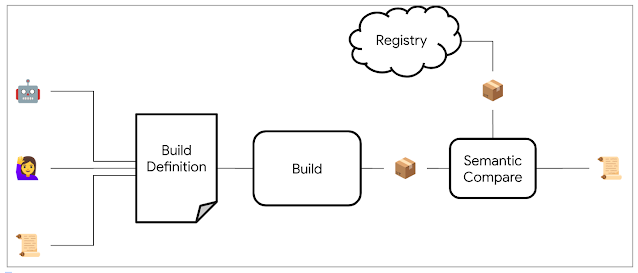
Google has launched OSS Rebuild, a new initiative aimed at exposing malicious code and strengthening software supply chain security across major open-source ecosystems like PyPI, npm, and Crates.io. |
Source: security.googleblog.com |
The project works by automatically rebuilding widely used packages using declarative definitions and comparing the results to upstream artifacts, flagging inconsistencies that may indicate tampering. Developers and security teams should look into the initiative as a way of reducing the risk of compromise, without adding burden to maintainers. |
CISA Orders Immediate Patching as Chinese Hackers Exploit SharePoint Flaws in Active Attacks
|
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an emergency directive requiring federal agencies to patch two newly exploited Microsoft SharePoint vulnerabilities by July 23.
These flaws, used in tandem for spoofing and remote code execution, are being actively weaponized by Chinese state-backed groups Linen Typhoon and Violet Typhoon to compromise on-premises SharePoint servers. Microsoft SharePoint users are advised to patch immediately to avoid being compromised. |
Coyote Malware Variant Hijacks Windows Accessibility Features to Steal Banking and Crypto Credentials |
A new variant of the Coyote banking trojan has become the first malware strain to abuse Windows’ UI Automation (UIA) framework to harvest sensitive financial data.
According to Akamai researchers, the malware targets Brazilian users by programmatically accessing login elements on banking and cryptocurrency websites tied to 75 institutions. By leveraging UIA—a feature meant for assistive technologies—the malware evades traditional detection methods while harvesting credentials directly from the user interface.
Admins are advised to watch for strange use of UIAutomationCore.dll, as this could signify a compromise. |
|
|
How is your confidence in today’s crypto security? |
|
|
Yesterday's Pulse Check Results |
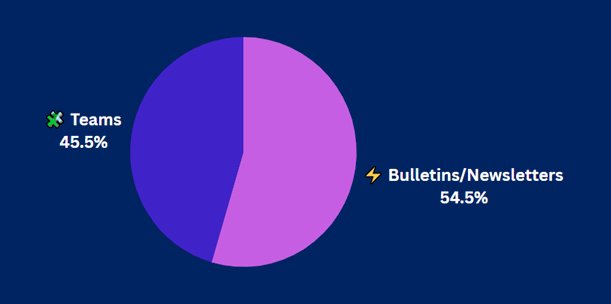
How do you stay ahead of critical patches and breaches? |
|
|
Security Tools You Can Use |
-
Gain visibility into your smartphones, servers, and all your other mobile devices with NinjaOne.
-
Build a strong first line of defense with this ready-to-use Antivirus Policy template that sets clear expectations for malware protection across your organization.
-
Check out the Best Cybersecurity Software for helping you cut through the noise and find the perfect digital bodyguard for your business.
|
|
|
Hackers Breach U.S. Nuclear Security Agency via SharePoint Zero-Day Exploit |
Unknown threat actors have breached the networks of the U.S. National Nuclear Security Administration (NNSA) by exploiting a recently patched Microsoft SharePoint zero-day vulnerability chain. |
The NNSA, responsible for maintaining the nation’s nuclear arsenal and managing radiological emergency response, confirmed the intrusion occurred on July 18.
While the Department of Energy stated the impact was minimal due to its reliance on Microsoft 365 and strong cybersecurity measures, a small number of systems were affected and are currently being restored. Users should patch their Microsoft SharePoint packages, if they haven’t already done so. |
SysAid Flaws Are Being Actively Exploited to Hijack Admin Accounts, Patch Immediately |
CISA has issued a warning about active exploitation of two critical XML External Entity (XXE) vulnerabilities in SysAid ITSM software, which allow attackers to hijack administrator accounts.
These unauthenticated flaws can be trivially exploited to access sensitive files, as demonstrated by public proof-of-concept code. CISA has added the flaws to its Known Exploited Vulnerabilities Catalog and mandated federal agencies to patch by August 12. Organizations beyond the public sector are also strongly urged to prioritize remediation. |
|
|
Keep Your Software Updated and Reduce Your Risk Exposure |
Patch management is a critical defense mechanism against the rise of ransomware, malware, and data breaches. However, many users and organizations delay this critical process to avoid disrupting operations, leaving critical systems exposed and often non-compliant with industry regulations. |
Proper patch management requires a balance of vigilance, oversight, and strategy—one that can be achieved with the following tips: |
- Prioritize critical security updates using CVSS/CVE scores to address the most dangerous vulnerabilities first.
- Maintain an up-to-date asset inventory to know exactly what software and hardware needs patching.
- Document patching activities for compliance reporting and audit purposes.
-
Monitor patch release cycles, such as Microsoft’s Patch Tuesday, to plan updates accordingly.
- Review and improve the patching strategy regularly to adapt to new threats and organizational changes.
|
By following these basics, you can significantly reduce risk, ensure compliance, and maintain resilient, secure operations of your software systems. |
|
|
| Leon Yen is a cybersecurity expert and seasoned tech journalist with over a decade of experience, including founding a cyber risk startup and leading industry-focused research and reporting. |
|
|
Protect your team with premium policies, guides, and more |
Cybersecurity Insider subscribers can now get 20% off an annual subscription to TechRepublic Premium and unlock unlimited access to hundreds of customizable policy templates, step-by-step checklists, and expert-written guides. Replace days of research and drafting with proven, plug-and-play resources that help your team harden defenses and stay audit-ready — fast. Use the code CSI20 at checkout. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|