Stay sharp out there, Digital Defenders. |
A critical NVIDIAScape vulnerability puts NVIDIA’s AI container toolkit at risk, Iranian spyware is lurking behind fake VPNs and banking apps, and Dell has confirmed a ‘World Leaks’ cyberattack on its test lab platform. |
|
| Here’s what you need to know: |
|
|
‘NVIDIAScape’ Critical Vulnerability Exposed in NVIDIA’s AI Container Toolkit |
Researchers from Wiz have uncovered NVIDIAScape (CVE-2025-23266)—a critical flaw in NVIDIA’s Container Toolkit (NCT) that lets attackers break out of isolated AI containers and gain full root access on the host machine.
Versions affected: NCT up to 1.17.7 and NVIDIA GPU Operator versions up to 25.3.0. |
Source: Unsplash / Mariia Shalabaieva |
With a CVSS score of 9.0 (Critical), the bug threatens managed AI cloud services where customers can run their own AI containers on shared GPU infrastructure. A malicious customer can deploy a specially crafted container, escape its boundaries, and potentially steal sensitive data from all other customers on the same shared hardware.
Wiz warns that exploits like NVIDIAScape disrupt the AI ecosystem, as NCT powers many managed AI and GPU services from major cloud providers.
Upgrade to the latest version of NCT immediately, as per the latest NVIDIA Security Bulletin. |
Cisco Patches Identity Services Vulnerabilities Enabling Root-Level Attacks |
Cisco has released patches for three vulnerabilities in its Identity Services Engine (ISE) and Cisco ISE Passive Identity Connector (ISE-PIC) that could allow an unauthenticated remote attacker to achieve arbitrary code execution with root privileges. Vulnerabilities addressed: |
- CVE-2025-20281 and CVE-2025-20337: Open Cisco ISE and ISE-PIC to remote code execution.
- CVE-2025-20282: Exposes ISE and ISE-PIC Release 3.4 to arbitrary code execution or root-level compromise.
|
419K Louis Vuitton Customers in Hong Kong Affected by Data Breach |
Luxury brand Louis Vuitton has been hit with a data leak impacting roughly 419,000 customers in Hong Kong, with signs of related incidents surfacing in South Korea and the United Kingdom.
According to Hong Kong’s Office of the Privacy Commissioner for Personal Data, the exposed information includes names, passport details, addresses, phone numbers, email addresses, and shopping history.
If you’ve shopped with LV lately, we recommend resetting your account credentials and staying alert for unusual activity or phishing attempts. |
|
|
How do you stay ahead of critical patches and breaches? |
|
|
Yesterday's Pulse Check Results |
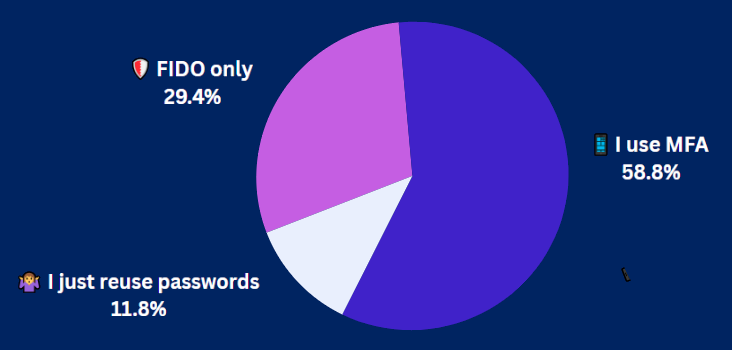
How locked down is your MFA setup—really? |
|
|
Security Tools You Can Use |
|
|
Iranian Spyware Disguised as VPNs and Banking Apps to Steal Data |
Researchers at Lookout have discovered new variants of DCHSpy, a surveillance tool on Android masquerading as VPNs and banking apps to harvest user information. |
Source: Unsplash / Onur Binay |
Believed to be operated by Iranian cyberespionage group MuddyWater, DCHSpy has been on Lookout’s radar since 2024. According to their findings, new versions of the surveillanceware surfaced just a week after the recent Israel-Iran conflict, targeting adversaries. Once installed, the malware collects SMS messages, call logs, location data, audio recordings, photos, and more.
Users should only download VPNs from reputable providers and avoid installing APKs from third‑party sources. |
Dell Confirms ‘World Leaks’ Cyberattack on Test Lab Platform |
Dell has confirmed that its Customer Solution Centers platform was recently hit by a ransomware attack and extortion attempt from the World Leaks hacker group.
The company says the breach does not involve customer data, as the platform relies on synthetic and publicly available datasets to demonstrate products and services for commercial clients.
Experts warn this could signal a growing trend of hackers targeting test environments, pressuring companies to pay ransoms to avoid reputational damage. Organizations operating demo environments should review security controls and monitor them closely for suspicious activity. |
|
|
Outsmart Ticket Scams and Consumer Fraud |
Consumer scams are on the rise, with scammers now leveraging AI tools to craft fake purchase emails to trick victims into downloading malware-infested apps. This same playbook is increasingly being used in the ticket market for concerts, festivals, and other live events, where scammers prey on trust and urgency to carry out social‑engineering schemes.
|
Source: Unsplash / Xie lipton |
Experts at eSecurityPlanet highlighted key security recommendations from PayPal and Venmo to help you stay protected: |
-
Use purchase protection offered by trusted payment platforms like PayPal and Venmo.
- Buy only from verified sellers and avoid sketchy listings on social media.
- Stay alert to suspicious payment methods, as scammers often push for wire transfers or crypto.
-
Look for red flags such as strange links, generic greetings, and fake “limited‑time” offers designed to rush you.
|
By following these tips, you can keep your transactions safe and enjoy your next event without worry. |
|
|
| Senior Staff Writer at TechnologyAdvice |
Luis Millares is a seasoned tech writer with broad experience reviewing consumer gadgets and enterprise software, offering clear, reliable insights across the latest in technology. |
|
|
Protect your team with premium policies, guides, and more |
Cybersecurity Insider subscribers can now get 20% off an annual subscription to TechRepublic Premium and unlock unlimited access to hundreds of customizable policy templates, step-by-step checklists, and expert-written guides. Replace days of research and drafting with proven, plug-and-play resources that help your team harden defenses and stay audit-ready — fast. Use the code CSI20 at checkout. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|