Cybercrime’s on the value menu, Digital Defenders. |
In today’s rundown: McDonald’s hiring system leaks data on 64 million applicants, Microsoft patches a nasty SQL Server RCE, and Nova Scotia Power’s ransomware hit is disrupting its power meter readings. |
|
|
Here’s what you need to know: |
|
|
Fast Food, Slow Security: McDonald's Hiring Platform Leaks 64M Job Seeker Records |
McDonald’s AI-powered hiring platform—McHire—has exposed the personal data of 64 million job applicants due to alarmingly weak security practices. |
Source: Unsplash / Road Ahead |
Security researchers uncovered critical vulnerabilities in the platform—most notably the use of “123456” as both username and password to access applicant databases. The exposed data includes applicant names, email addresses, chat histories, and phone numbers.
Built by Paradox.ai, McHire was also found to lack basic protections such as multi-factor authentication and was susceptible to simple dictionary attacks.
If your org relies on third-party platforms for hiring or data intake, ensure they meet modern security standards like MFA and password complexity. |
Patch Tuesday: Microsoft Fixes SQL Server RCE, 136 Other Vulnerabilities |
Microsoft recently patched 137 vulnerabilities, including CVE-2025-49719—a high-severity vulnerability which allowed remote code execution in SQL Server.
The security flaw could let unauthenticated threat actors extract uninitialized memory by submitting crafted queries. While Microsoft says no active exploitation has been observed, the availability of a proof-of-concept exploit significantly increases the risk of an attack.
Organizations using Microsoft SQL Server should apply the latest patches without delay. To better understand how to protect against similar threats, review this guide on SQL Injection Prevention. |
Privacy Grounded: Qantas Confirms Major Data Leak Impacting 1M Flyers |
Following last week’s breach disclosure, Qantas has now confirmed that the personal data belonging to over 1 million customers—including phone numbers, addresses, and birth dates—has been compromised. Another 4 million had only their names and email addresses compromised.
Loyalty platforms and customer portals are prime targets—ensure your org’s reward programs and login flows are hardened against credential stuffing and token theft. |
|
|
Where do you put your trust for secure storage? |
|
|
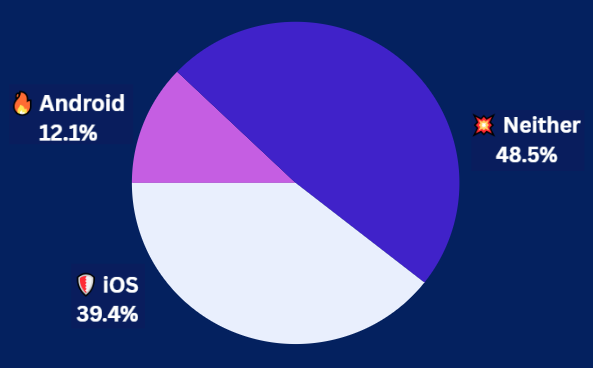
Yesterday's Pulse Check Results |
Which mobile platform do you trust more for security? |
|
|
Security Tools You Can Use |
|
|
Static Shock: Ransomware Attack Blocks Nova Scotia Power Meter Readings |
A ransomware attack, stemming from a cyber incident on April 25, has prevented Canadian electricity provider Nova Scotia Power from properly recording meter readings—disrupting billing processes for its customers. |
Source: Unsplash / Jon Moore |
According to the company, the cyberattack interfered with power meters, blocking them from transmitting usage data to their internal systems. The incident impacted approximately 280,000 Canadians, potentially exposing customer names, phone numbers, service addresses, and driver’s license numbers.
This attack underscores how ransomware can disrupt physical operations—monitor telemetry systems and prioritize recovery testing |
‘NightEagle’ exploits Exchange zero-day in espionage campaign |
NightEagle, a North American-based APT, is actively exploiting a zero-day in Microsoft Exchange to exfiltrate sensitive data from China’s technology and defense industries.
Researchers at Qianxin Technology's RedDrip Team uncovered the campaign, which uses a trojanized version of open-source tunneling tool Chisel to gain unauthorized remote access via compromised Exchange email servers.
Microsoft Exchange users should monitor for official security updates, as the company continues its investigation into the alleged vulnerability. |
|
|
Avoid Cracked or Pirated Game Downloads |
Pirated games might promise free fun, but many come with a hidden cost—malware. Threat actors are increasingly weaponizing cracked game downloads to infect gamers with info-stealing payloads.
As Yahoo Tech reports, some of these malicious installers even feature fake CAPTCHA portals to appear safe and trustworthy. However, once a gamer hits download, they get info-stealing malware instead. |
Source: Unsplash / Alex Haney |
Here’s how to stay safe from malware-infected game downloads: |
- Skip the cracked game versions, especially for popular titles that are a prime bait for attackers.
- Don’t ignore security warnings from your OS or your antivirus software.
- Be skeptical of fake verification pages that try to add false legitimacy.
-
Avoid installing mysterious software, particularly when perusing “free game” sites.
|
Don’t trade your identity for a free game. Use official stores to stay malware-free. |
|
|
| Senior Staff Writer at TechnologyAdvice |
Luis Millares is a seasoned tech writer with broad experience reviewing consumer gadgets and enterprise software, offering clear, reliable insights across the latest in technology. |
|
|
Protect your team with premium policies, guides, and more |
Cybersecurity Insider subscribers can now get 20% off an annual subscription to TechRepublic Premium and unlock unlimited access to hundreds of customizable policy templates, step-by-step checklists, and expert-written guides. Replace days of research and drafting with proven, plug-and-play resources that help your team harden defenses and stay audit-ready — fast. Use the code CSI20 at checkout. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|