Your Friday intel drop is here, Digital Defenders. |
Today’s updates show how even cutting-edge tech can become a liability. Scale AI leaked sensitive files, AI agents are slipping past enterprise safeguards, and hackers are weaponizing trusted open-source tools. Trust, once broken, is hard to patch. |
|
|
Here’s what you need to know: |
|
|
Scale AI Leak: Sensitive Docs from Google, Meta, xAI Go Public |
Scale AI is in hot water after reportedly leaking sensitive internal data for its clients—including Meta, Google, and xAI—via unsecured Google Docs.
According to TechRepublic, citing a Business Insider report, Scale AI used public Google Docs that were accessible to anyone with a direct link. This included 85 exposed documents, some of which were editable and marked “confidential,” containing training data, internal documents, and project materials for its high-profile tech partners. |
US Sounds Alarm on Iranian Cyber Threats Amid Escalating Middle East Tensions |
The US Department of Homeland Security (DHS) has issued a national terrorism advisory bulletin warning of likely cyber activity by pro-Iranian hackers in response to recent US airstrikes on Iranian nuclear sites. High-profile organizations: Stay on high alert and tighten endpoint defenses immediately.
|
Study: AI Agents Pose Hidden Risks to Enterprise Security |
| |
What’s your stance on AI agents in the workplace? |
|
|
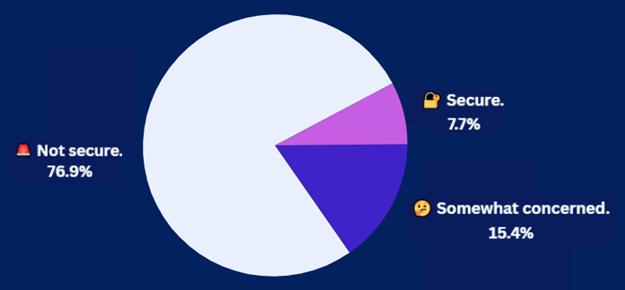
Yesterday's Pulse Check Results |
Messaging apps are a growing target. How safe is yours? |
|
|
Security Tools You Can Use |
|
|
Open-Source Attacks Threaten Africa’s Financial Industry |
Unit 42 researchers have uncovered a new campaign targeting financial businesses in Africa, with the hackers leveraging open-source tools to carry out their attacks. |
According to Unit 42, threat actors are leveraging open-source and publicly available tools, including PoshC2, Chisel, Microsoft’s PsExec, and Classroom Spy, to steal user credentials and infect targeted networks. Finance Teams: Stay vigilant by auditing network activity and monitoring for signs of unauthorized access.
|
British Hacker ‘IntelBroker’ Charged in $25M Cybercrime Case |
UK-based hacker Kai West, known as “IntelBroker,” has been charged by the US for allegedly stealing and selling sensitive data from government agencies, critical infrastructure, and major corporations in the US.
According to Bleeping Computer, West routinely listed stolen data on the BreachForums hacking site. His attacks have been linked to breaches at Nokia, AMD, General Electric, and Europol, with damages totaling an estimated $25 million. Don’t wait to discover a breach: Set up real-time Dark Web alerts to catch exposed credentials before attackers act. |
|
|
Time is critical—don’t panic! Semperis enables Active Directory recovery 90% faster than manual methods, saving organizations an average of $3.9 million over 3 years. Rapid recovery helps you resist ransomware, which disrupts 87% of victims. Say “No!” to downtime and data loss with Semperis—your AD recovery safety net. |
|
|
Delay an Update, Invite a Breach |
Receiving OS update notifications may feel like a hassle, but it’s time to treat them as critical security measures that keep your data safe, secure, and out of hackers’ hands.
Case in point: Earlier this month, Google rolled out a security patch fixing over 30 vulnerabilities in Android devices. As it turns out, OS updates aren’t just for fancy new themes or capabilities. They often patch real threats. |
Source: Unsplash / Azamat E |
Here’s why you should tap that “Update OS” button sooner rather than later: |
-
Patch critical vulnerabilities: OS updates often fix bugs actively exploited by threat actors.
- Close security gaps: They seal off flaws that could give hackers access to your data.
- Enhance performance and features: Major updates can improve your device's speed and introduce new capabilities.
-
Ensure app compatibility: Updates keep your system aligned with the latest apps for a smoother, safer experience.
|
More often than not, a single tap on “Update” is all it takes to keep your mobile data out of a hacker’s hands. |
|
|
| Senior Staff Writer at TechnologyAdvice |
Luis Millares is a seasoned tech writer with broad experience reviewing consumer gadgets and enterprise software, offering clear, reliable insights across the latest in technology. |
|
|
Into more than just malware and mayhem?
|
Stay sharp on AI, cloud, DevOps, and the tech players shaking things up. Subscribe to Daily Tech Insider for no-fluff rundowns and witty breakdowns delivered straight to your inbox—because knowing what’s next helps you stay secure. |
|
|
Into more than just malware and mayhem? |
Stay sharp on AI, cloud, DevOps, and the tech players shaking things up. Subscribe to Daily Tech Insider for no-fluff rundowns and witty breakdowns delivered straight to your inbox—because knowing what’s next helps you stay secure. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|