It’s time to level up, Digital Defenders! 🛡️ |
Today’s security updates serve up a triple threat: food supply chaos, breached crash reports, and hackers stirring up trouble just for kicks. Plus, an old Google account recovery form has a glaring flaw.
Also, be sure to check out our poll at the bottom: How secure is your cloud storage setup? |
|
| Here’s what you need to know: |
|
|
Google Flaw Exposed Phone Numbers With Just a Name |
Security researcher BruteCat uncovered a vulnerability in an outdated version of Google’s account recovery form that allowed attackers to brute-force users’ full recovery phone numbers using only a profile name and a partial number. |
Since most people reuse their recovery number as their primary contact, this flaw could have enabled large-scale account hijacking campaigns before it was patched. Interestingly, Google didn’t consider this a serious flaw but has since patched the vulnerability. To protect your accounts, review account recovery settings regularly for outdated or overly exposed information. |
Sensata Confirms Data Breach Impacting Employees, Dependents |
Sensata Technologies has confirmed that a ransomware attack resulted in a significant data breach, compromising sensitive personal information of current and former employees, as well as their dependents.
The global industrial tech firm said attackers had over a week of unauthorized access, stealing files with SSNs, financial data, and medical records. It’s now notifying victims and offering a year of credit monitoring and identity protection. If you’re affected, take advantage of the offer and regularly monitor your accounts for suspicious activity. |
Arkana Gang Recycles Snowflake-Stolen Data in Fake Ticketmaster Leak |
The Arkana extortion group recently caused a stir by claiming to sell 569 GB of newly stolen Ticketmaster data. However, cybersecurity investigators have confirmed that it's recycled data from the 2024 Snowflake breach.
The post included screenshots and references to "RapeFlake," a custom tool used in the original attacks carried out by ShinyHunters, who exfiltrated data from several high-profile companies using stolen Snowflake credentials. Remember to take precautions in verifying breach claims, as threat actors often recycle old data to incite panic and bolster their image. |
|
|
-
NinjaOne enables IT teams to secure their environment, streamline patching, and manage every endpoint all from a single, intuitive dashboard.
-
Learn how to spot the red flags of a phishing email early to keep your business protected from costly data breaches.
|
|
|
Hackers Hit Whole Foods’ Main Supplier, Causing Delivery Delays |
United Natural Foods, the primary supplier for Whole Foods and one of the largest health food distributors in North America, disclosed a cyberattack that began on June 5 and has disrupted its ability to fulfill customer orders. |
In filings with the SEC and a public statement, the company stated that it took its systems offline after detecting unauthorized activity, resulting in ongoing operational delays. Workarounds are in place, and law enforcement has been notified as the investigation continues.
This incident adds to a growing list of cyberattacks targeting the food and agriculture sector, which has seen repeated disruptions to major supply chains in recent years. To stay well-prepared, be vigilant for service disruptions as cyberattacks targeting the food and agriculture sectors increase. |
Texas DOT Breach Exposes Nearly 300,000 Crash Reports |
The Texas Department of Transportation (TxDOT) confirmed a data breach that led to the theft of nearly 300,000 detailed crash reports from its Crash Records Information System (CRIS).
Discovered on May 12, the breach stemmed from a compromised account used to access sensitive records containing names, addresses, driver’s license numbers, insurance details, injury reports, and crash narratives. Though not legally required to notify the public, Texas is contacting affected individuals and urging caution against potential scams.
Watch for phishing attempts using crash data, enable two-factor authentication, and consider placing a fraud alert if your info was involved. |
Cybercriminals Shift from Bulletproof Hosting to Proxies to Evade Crackdowns |
As law enforcement ramps up pressure on bulletproof hosting services long favored by cybercriminals, threat actors are increasingly migrating to proxy-based infrastructures to stay hidden.
A researcher at Sleuthcon revealed how purpose-built VPNs and residential proxies are becoming the new go-to for masking malicious traffic, offering anonymity by blending criminal activity with legitimate user data. To stay secure, be cautious of the networks you use, as cybercriminals increasingly hide behind custom VPNs and proxies to evade detection. |
|
|
Lock Down Your Cloud Before Hackers Move In |
No one can deny that cloud storage makes managing your digital life significantly easier. But don’t get sloppy: hackers are constantly hunting for weak spots to snatch your data.
And be sure to stay informed about product updates—sometimes, even cloud providers roll out new features that unintentionally create new security risks. |
Here are a few practical guidelines to enhance your cloud security and safeguard your data: |
-
Upload sensitive data only to accounts with MFA.Encrypt your connection to block eavesdropping.
- Never store passwords in the cloud; use a password manager.
- Encrypt files before uploading.
- Lock down sharing permissions.
- Use strong, unique passwords and change them often.
- Keep your cloud tidy; control auto-sync.
- Back up your backups on multiple platforms.
- Avoid public or shared devices; always log out.
|
Remember: your data is only as safe as your weakest link. |
|
|
Security Question of the Day |
How secure is your cloud storage setup? |
|
|
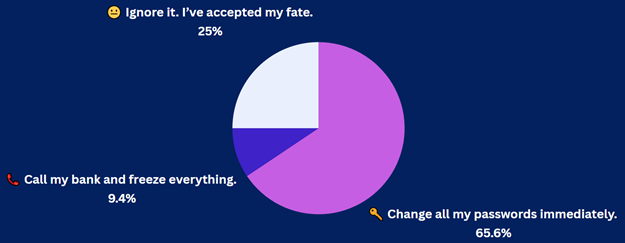
Results from Yesterday's Security Question of the Day |
What’s your post-breach panic move? |
|
|
| Leon Yen is a cybersecurity expert and seasoned tech journalist with over a decade of experience, including founding a cyber risk startup and leading industry-focused research and reporting. |
|
|
Into more than just malware and mayhem? |
Stay sharp on AI, cloud, DevOps, and the tech players shaking things up. Subscribe to Daily Tech Insider for no-fluff rundowns and witty breakdowns delivered straight to your inbox—because knowing what’s next helps you stay secure. |
|
|
Into more than just malware and mayhem? |
Stay sharp on AI, cloud, DevOps, and the tech players shaking things up. Subscribe to Daily Tech Insider for no-fluff rundowns and witty breakdowns delivered straight to your inbox—because knowing what’s next helps you stay secure. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|