Brace yourselves, Digital Defenders! 🛡️ |
Cyber crooks are weaponizing conversations, human and AI alike. From vishing scams to court battles over deleted ChatGPT chats, your words are becoming attack vectors. Think before you speak (or type). Get ahead, and don’t forget to answer our poll at the bottom: How secure is your personal AI usage? |
|
|
Here’s what you need to know: |
|
|
OpenAI Fights to Keep Your Deleted Chats Private |
OpenAI is challenging a court order to preserve all ChatGPT user logs, including deleted and sensitive API chats, after news organizations accused the tech giant of destroying evidence in a copyright lawsuit. |
The company argues the order was issued without just cause and threatens the privacy of hundreds of millions of users across its Free, Plus, Pro, and API services. The judge sided with plaintiffs who feared deleted chats hid evidence of paywall bypasses, prompting the order to preserve all logs. Avoid sharing sensitive information in AI conversations, as deleted ChatGPT chats may still be subject to legal review. |
Google Unmasks Vishing Crew Hijacking Salesforce to Steal and Extort at Scale |
Google’s Threat Intelligence Group has identified a financially motivated threat actor, dubbed UNC6040, which uses sophisticated voice phishing (vishing) tactics to compromise corporate Salesforce environments.
Posing as IT support, attackers trick employees into approving a fake Salesforce Data Loader app, then steal data for extortion and pivot to access Okta, Microsoft 365, and Workplace. The campaign shows how social engineering and app abuse are converging to breach even well-defended systems.
Always verify IT support requests through official channels and never approve unknown apps or tools, especially those requesting access to sensitive platforms like Salesforce. |
FBI Says ‘Play’ Ransomware Has Hit 900 Victims and Keeps Evolving |
The FBI, in a joint advisory update with CISA and Australian cyber authorities, revealed that the Play ransomware gang has compromised around 900 organizations as of May 2025—triple the number reported in 2023.
Active since 2022, Play has targeted businesses and critical infrastructure across the Americas and Europe, often using recompiled malware to evade detection. Its evolving tactics and global reach make it one of the most persistent ransomware threats in today.
Because recent attacks used phone threats and RMM exploits to plant Sliver beacons, users should be sure to patch their systems and watch for unusual remote access. |
|
|
Malicious GitHub repos hide backdoors as hacking tools |
Sophos has uncovered a stealthy malware campaign in which a threat actor lures hackers, gamers, and researchers with GitHub-hosted tools, such as exploits and game cheats, that secretly install backdoors. |
The bait often includes non-functional code, such as Sakura RAT, which leverages Visual Studio PreBuild events to install malware during compilation. Tied to over 140 repos, the attacker hides obfuscated payloads in Python, JavaScript, and .scr files, using fake commits to appear legitimate.
Always inspect GitHub code before compiling, avoid running unverified tools from unknown sources, and watch for suspicious project activity like frequent automated commits. |
Cisco Patches Critical Cloud Credential Flaw in Identity Services Engine |
Cisco has issued fixes for several exploited vulnerabilities, including a critical flaw (CVE-2025-20286) in its Identity Services Engine (ISE) that affects cloud deployments on AWS, Azure, and Oracle Cloud. Due to improperly generated static credentials, unauthenticated attackers could access other cloud-based ISE instances, enabling them to steal data, alter configurations, or disrupt services. The flaw affects cloud-based Primary Admin nodes, with public exploit code available. If you use cloud-based ISE, apply the patch now, and rotate any static credentials to block potential backdoor access. |
Lee Enterprises Ransomware Breach Exposes Data of Nearly 40,000 Individuals |
Publishing giant Lee Enterprises is alerting 39,779 people that their data, including names and Social Security numbers, was stolen in a February 2025 ransomware attack.
The breach, which crippled internal systems and disrupted newspaper printing and delivery across 26 states, forced the company offline as attackers accessed sensitive documents. Lee’s broad reach as one of the largest U.S. media groups made the attack especially disruptive, crippling VPNs, cloud access, and newsrooms nationwide.
To stay protected, monitor your personal data for suspicious activity and consider freezing your credit if your Social Security number was exposed. |
|
|
We want to hear from you!
We are conducting a survey to gauge awareness of Cisco Secure. Your input will contribute to valuable insights about the brand recognition and familiarity of the solution provider.
We understand that your time is valuable, so we kept our survey as short as possible - just answer 4 questions! The survey will take approximately 2 minutes or less to complete. |
|
|
AI Is a Beast. Here’s How to Tame It Before It Bites You |
Chatbots like ChatGPT have flipped the script on how we create, communicate, and hustle. They’re game changers. But with that power comes a dark side. Drop your guard, and you risk exposing sensitive info or handing over your data to faceless algorithms hungry for training fuel. |
If you want to stay ahead, lock down your AI use before it turns your secrets into someone else’s advantage. |
Here are some critical tips for securing your AI use: |
- Never share passwords, SSNs, or PINs. If it’s private, keep it offline.
- Ditch public Wi-Fi or always use a VPN when chatting with AI to block prying eyes.
-
Turn off the “Improve The Model” options in your AI settings to prevent your conversations from contributing to future training data.
- Regularly delete your chat history. Don’t let your past slip into the AI’s memory banks.
- Disable your chat history entirely for total peace of mind.
|
Remember: These platforms aren’t Fort Knox. Even the most sophisticated AI models can’t guarantee that your information won’t leak or be used in ways you never intended. |
|
|
Security Question of the Day |
How secure is your personal AI usage? |
|
|
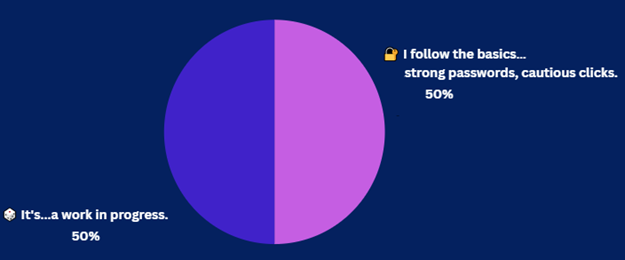
Results from Yesterday's Security Question of the Day |
Be honest: how’s your crypto hygiene?
|
|
|
| Leon Yen is a cybersecurity expert and seasoned tech journalist with over a decade of experience, including founding a cyber risk startup and leading industry-focused research and reporting. |
|
|
Into more than just malware and mayhem? |
Stay sharp on AI, cloud, DevOps, and the tech players shaking things up. Subscribe to Daily Tech Insider for no-fluff rundowns and witty breakdowns delivered straight to your inbox—because knowing what’s next helps you stay secure. |
|
|
Into more than just malware and mayhem? |
Stay sharp on AI, cloud, DevOps, and the tech players shaking things up. Subscribe to Daily Tech Insider for no-fluff rundowns and witty breakdowns delivered straight to your inbox—because knowing what’s next helps you stay secure. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|