Get ready, Digital Defenders! 🛡️ |
Your phone. Your code. Your dog’s collar. All fair game. From Chrome zero-days to crypto scams and credential theft, today’s threats strike fast… and hit home. Get the full picture below, and don’t forget to answer our poll at the bottom: Is your pet a walking smart gadget? |
|
|
Here’s what you need to know: |
-
Google issues urgent patch for third Chrome zero-day of 2025
- Qualcomm rushes to patch spyware-ready zero-days
- Crypto miners hijack Docker and Nomad in first-ever wild exploit
- The North Face suffers major data breach
- Cartier confirms customer information exposed in cyberattack
|
|
|
Another Chrome Emergency: Zero-Day Exploit Hits Again |
The high-severity flaw, discovered by Google’s own Threat Analysis Group, stems from an out-of-bounds read/write bug in Chrome's V8 JavaScript engine. Attackers are already exploiting the bug in the wild, potentially putting millions of users at risk of silent compromise through malicious web content. If you haven’t updated Chrome yet, do it now. This patch closes an open door that's actively being used. |
Spyware Vendors Are Weaponizing Qualcomm Zero-Days |
Qualcomm has released security updates to fix three zero-day vulnerabilities in its Adreno GPU drivers, all of which have been exploited in limited, targeted attacks.
Discovered by Google’s Android Security team, the flaws include two high-severity authorization bugs, all of which can trigger memory corruption. These flaws echo past GPU-related vulnerabilities leveraged by spyware vendors, raising concerns about potential surveillance abuse. Users should ensure their devices receive the latest security updates promptly and avoid installing apps from untrusted sources. |
New Cryptojacking Campaign Hijacks Docker, Gitea, and HashiCorp Nomad |
Researchers at Wiz have uncovered a stealthy cryptojacking operation, dubbed JINX-0132, that targets misconfigured DevOps tools—including Docker, Gitea, and HashiCorp Nomad—for illicit cryptocurrency mining.
In what is believed to be the first documented abuse of Nomad misconfigurations in the wild, attackers are leveraging public GitHub repositories to stage their payloads, thereby complicating attribution.
To mitigate risk, organizations should audit their DevOps environments for misconfigurations, apply security patches promptly, and restrict public access to sensitive services, such as Nomad and Docker. |
|
|
- Explore how NinjaOne’s unified platform helps IT teams tighten security, automate patching, and take control of every endpoint from one dashboard.
-
Need consistent DNS and DHCP rules? Get started quickly with this ready-to-use DNS and DHCP Usage Policy to streamline your IT management efforts.
|
|
|
The North Face Warns Customers of Data Breach After Credential Stuffing Attack | The attack involved cybercriminals using previously leaked username and password combinations to break into accounts, a tactic made easier by password reuse.
The company has begun notifying affected customers and urges them to use multi-factor authentication to prevent future breaches. |
Cartier Breach Exposes Customer Data in Targeted Cyber Attack |
Luxury brand Cartier has disclosed a data breach after hackers gained temporary access to its systems and stole customer information, including names, email addresses, and country of residence. The incident was contained, and the company says it has since strengthened its security measures.
While Cartier assures that no passwords or financial data were compromised, it warns customers to stay alert for phishing attempts or suspicious messages. |
Russian Market Surges as Top Hub for Stolen Credentials After Genesis Takedown |
The “Russian Market” cybercrime marketplace has become a go-to destination for buying and selling stolen credentials, filling the void left by the takedown of Genesis Market.
According to ReliaQuest, the platform has recently experienced a surge in popularity, offering infostealer logs that contain passwords, cookies, credit card data, and more, often for as little as $2. To protect against credential theft, users should enable multi-factor authentication, use a reputable password manager, and regularly scan their devices for infostealer malware. |
| |
We want to hear from you!
We are conducting a survey to gauge awareness of Cisco Secure. Your input will contribute to valuable insights about the brand recognition and familiarity of the solution provider.
We understand that your time is valuable, so we kept our survey as short as possible - just answer 4 questions! The survey will take approximately 2 minutes or less to complete. |
|
|
Don’t Let Your Best Friend Become Your Biggest Cyber Threat |
Smart pet gadgets are everywhere. Approximately 83% of pet owners in North America and Europe own at least one. GPS collars, voice-activated feeders, treat-launching cameras—they promise convenience and peace of mind.
But every connected device is a potential entry point for cybercriminals. That cute camera or feeder? It could be serving up your network credentials. |
Stay one step ahead with a few simple habits: |
-
Update everything: Keep pet devices and apps up to date to patch security holes.
- Use strong passwords: Unique, complex passwords, plus two-factor authentication (2FA), go a long way.
- Lock down your WiFi: Use WPA2/WPA3, change default logins, and update your router.
-
Check permissions: Only allow what’s necessary; review after updates.
- Buy smart: Stick to reputable brands—cheap tech can cost you your privacy.
|
That shiny new gadget might be fun, but a hacked home is anything but. Lock it down. |
|
|
Security Question of the Day |
Is your pet a walking smart gadget? |
|
|
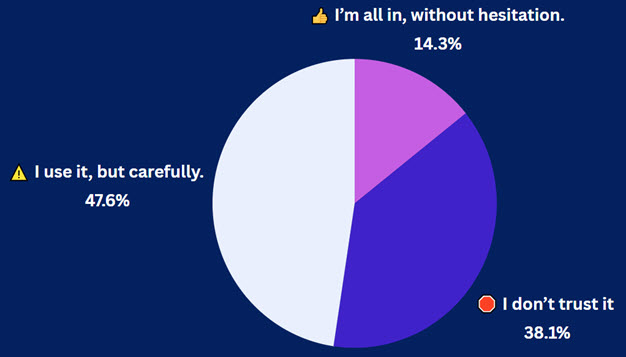
Results from Yesterday's Security Question of the Day |
What’s your take on AI-generated code? |
|
|
| Leon Yen is a cybersecurity expert and seasoned tech journalist with over a decade of experience, including founding a cyber risk startup and leading industry-focused research and reporting. |
|
|
Into more than just malware and mayhem? |
Stay sharp on AI, cloud, DevOps, and the tech players shaking things up. Subscribe to Daily Tech Insider for no-fluff rundowns and witty breakdowns delivered straight to your inbox—because knowing what’s next helps you stay secure. |
|
|
Into more than just malware and mayhem? |
Stay sharp on AI, cloud, DevOps, and the tech players shaking things up. Subscribe to Daily Tech Insider for no-fluff rundowns and witty breakdowns delivered straight to your inbox—because knowing what’s next helps you stay secure. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|