Heads up, Digital Defenders! 🛡️ |
Cybercriminals are breaking trust at every turn. Fake PayPal and DocuSign emails are stealing logins. Malware is tested to slip past trusted antivirus tools. Even AI is speeding up attacks faster than most teams can respond. How much trust do you put in AI-written code? Don’t miss the poll at the end. |
|
|
Here’s what you need to know: |
|
|
PayPal and DocuSign Phishing Scams Surge |
Source: ResolveTechNH / YouTube |
Security experts say these scams are becoming increasingly difficult to spot, as threat actors are mimicking branding, formatting, and even sender addresses. Once credentials are stolen, attackers can drain accounts, open lines of credit, or commit identity fraud.
Never click login links in unsolicited emails. Instead, open a new browser tab and navigate directly to the official site. Additionally, enable 2FA wherever possible to block account takeovers. |
US and EU Seize Domains Running Counter-Antivirus Services for Hackers |
In a coordinated global takedown, the U.S. Department of Justice and European partners seized four domains offering “crypting” and counter-antivirus (CAV) services that helped malware evade antivirus detection. The platforms enable hackers to upload malware and test it against dozens of antivirus engines, allowing them to tweak the code until it passes undetected.
Undercover agents confirmed the sites were actively used to aid cybercrime. The takedown is part of Operation Endgame, which recently disrupted Lumma Stealer, DanaBot, and hundreds of botnet servers.
If you're relying on public scanners for threat intel, assume adversaries are a step ahead and plan accordingly. |
CISA Teams Up with Australia on SIEM and SOAR Guidance |
CISA and the Australian Cyber Security Centre have released joint guidance to help organizations enhance their threat detection and response capabilities using SIEM and SOAR tools.
SIEM platforms collect log data from across a network to identify and flag suspicious activity. SOAR tools use that data to automate security workflows, combining alerts with predefined response playbooks. Together, they can streamline early detection and speed up incident response.
Although aimed at public agencies, various sectors should consider integrating platforms, prioritizing log sources, and aligning security automation with business continuity. |
|
|
-
Want to start a career in cybersecurity? This 14-page PDF guide covers certs, expert advice, and job-hunting strategies for just $19, or free with TechRepublic Premium.
-
Keeper Security offers secure storage, breach alerts, password sharing, and 24/7 support. Keep your digital life safe across all devices for just $3.33/month.
|
|
|
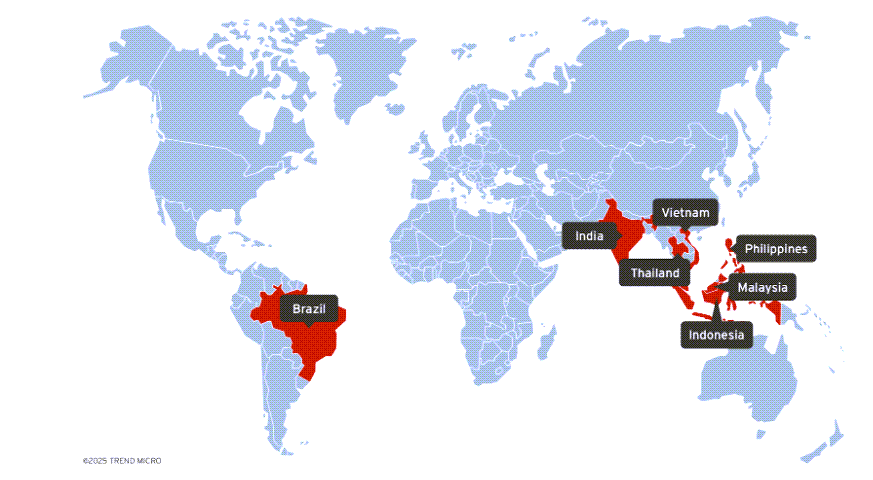
China’s ‘Earth Lamia’ Hijacks Open-Source Tools Across Asia |
Targets include universities, IT firms, and government agencies in India, Vietnam, Indonesia, and even Brazil. The group drops a custom backdoor called PulsePack to quietly extract data. Targets include universities, IT firms, and government agencies in India, Vietnam, Indonesia, and even Brazil. The group drops a custom backdoor called PulsePack to quietly extract data. Remember: Open-source doesn’t mean low-risk. Even free tools can fuel state-aligned campaigns. |
Cisco Flaw Lets Hackers Take Over Wireless Controllers |
A critical bug in Cisco IOS XE could let hackers fully control wireless network devices.
Researchers at Horizon3 found that when a certain feature is enabled, attackers can trick the system into accepting fake login tokens using a hardcoded password (“notfound”). By uploading files to the incorrect location, attackers can overwrite system settings and execute their own commands.
The issue affects Catalyst 9800 controllers with the Out-of-Band AP Image Download feature enabled. If your network uses Cisco gear, check for updates and disable unused features to reduce your exposure. |
AI Fuels Explosive Growth in Cyber Scans |
Automated cyberthreat scans are now hitting at 36,000 per second, with AI supercharging both the speed and scale of attacks. Threat actors are using AI to map vulnerabilities, evade detection, and launch mass probes at unprecedented volume.
The surge is global, but regions with outdated infrastructure or lax patching practices are being hit hardest. Experts warn that defensive automation must evolve just as fast—or faster—to keep up. Prioritize patching exposed assets and automate routine detection where possible. | |
|
Don’t Ship AI Code Without Security Review |
Google says 25% of its code is now AI-written, and many orgs are shipping AI-assisted changes straight to production without security sign-off. Without manual review or threat modeling, insecure defaults, exposed secrets, and vulnerable libraries can reach production unnoticed. |
Here are some tips on how to secure AI-powered dev: |
- Scan AI-generated code for insecure defaults before merge.
- Monitor for risky pull requests tied to legacy or sensitive services.ate info mid-flight.
- Require context tagging on AI-suggested code for traceability.
-
Automatically flag changes to critical systems made via code generation tools.
- Train devs to question AI outputs. “Looks good” isn’t secure.
|
Security can't be a speed bump. It has to be built into the driver’s seat. Embed security into the dev flow, not after. |
|
|
Security Question of the Day |
What’s your take on AI-generated code? |
|
|
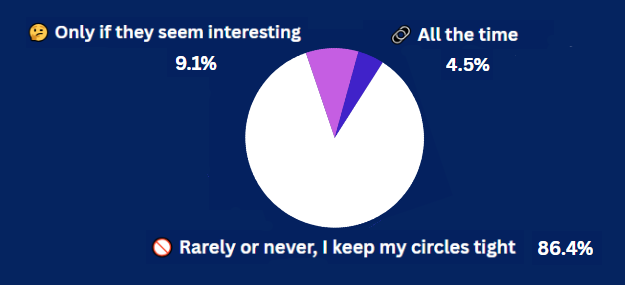
Results from Yesterday's Security Question of the Day |
How often do you accept friend or connection requests on social media? |
|
|
|
Greg Parker is a cybersecurity and emerging tech writer who explores the intersection of digital risk, human behavior, and innovation across sensing and security technologies. |
|
|
Into more than just malware and mayhem?
|
Stay sharp on AI, cloud, DevOps, and the tech players shaking things up. Subscribe to Daily Tech Insider for no-fluff rundowns and witty breakdowns delivered straight to your inbox—because knowing what’s next helps you stay secure. |
|
|
Into more than just malware and mayhem? |
Stay sharp on AI, cloud, DevOps, and the tech players shaking things up. Subscribe to Daily Tech Insider for no-fluff rundowns and witty breakdowns delivered straight to your inbox—because knowing what’s next helps you stay secure. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|