Welcome back, Digital Defenders! 🛡️ |
The breach reports are piling up. A compromised messaging app, VPNs under active attack, a telecom exploit on the dark web—and that’s just the start. Even Disney couldn’t escape the headlines this week. So, what’s currently moving the needle in cybersecurity? |
|
|
Here’s what you need to know: |
-
Government-used messaging app breached, archived data compromised
- SonicWall flaws under attack as hackers go after outdated VPNs
- Airline tied to ICE deportations breached, internal data exposed
- Man admits to stealing 1TB of Disney project files
|
| |
Messaging App Used by US Lawmakers Hacked |
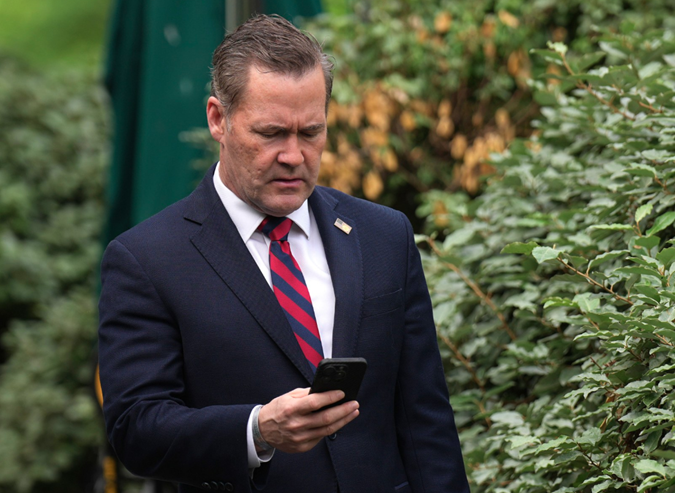
TeleMessage, a modified version of the Signal messaging app used by U.S. officials, including former National Security Advisor Mike Waltz, has been compromised.
Hackers accessed archived messages, contact info for Customs and Border Protection officers, and backend credentials. The root of the problem? These archived messages weren’t protected by end-to-end encryption. That missing layer left sensitive information wide open for attackers. |
Former National Security Advisor Mike Waltz Source: Newsweek |
If your organization relies on third-party secure messaging apps, check how archived content is stored and whether encryption is actually in place—not just advertised. |
SonicWall VPN Flaws Under Attack |
Two critical vulnerabilities in SonicWall’s SMA100 series VPN appliances are now being actively exploited in the wild, allowing attackers to execute arbitrary commands and read sensitive system files. Models 200, 210, 400, 410, and 500v are all affected. Although patches have been available since December 2023, many devices remain exposed.
Admins should immediately apply available updates and audit access logs for signs of compromise, especially if any devices have remained unpatched. |
67% Jump in Ransomware Attacks |
Ransomware and extortion incidents jumped 67% last year, according to NTT Security Holdings’ 2024 Global Threat Intelligence Report.
The report tracked more than 5,000 victims globally, up from around 3,000 in 2022. Attackers increasingly targeted the manufacturing, finance, and tech sectors. However, small businesses weren’t spared: Over half of the targeted organizations had fewer than 200 employees.
Now’s the time to double-check your backups, tighten access controls, and educate teams on the signs of an incoming attack. Ransomware isn't slowing down. |
|
|
GlobalX Airline Hacked After Deportation Flights Spark Backlash |
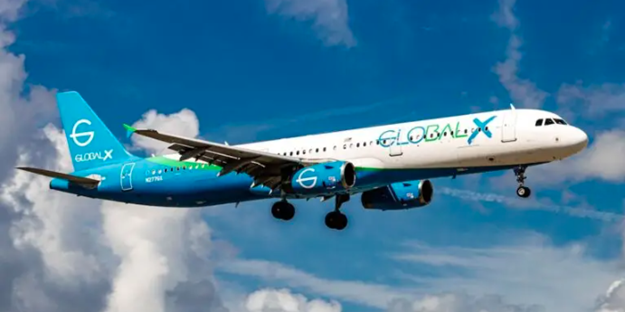
Hackers broke into GlobalX, a Florida-based charter airline known for handling deportation flights under the Trump administration.
The group behind the breach, claiming ties to Anonymous, leaked internal documents and defaced the company’s website. They say the hack was in protest of the airline’s involvement in deportations that allegedly violated court orders. |
Organizations operating in politically sensitive areas should expect to land on threat actors’ radar. Increased visibility often means increased risk, so make sure your defenses are ready for the spotlight. |
$5,000 Buys You an SS7 Exploit on the Dark Web |
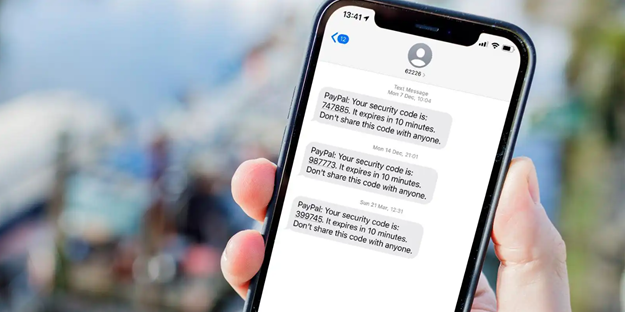
An unpatched SS7 protocol exploit is now for sale on the dark web—and it’s going for just five grand. The tool lets attackers intercept texts, eavesdrop on calls, and track phones in real time. SS7 is the decades-old protocol that still routes messages across global telecom networks, and it's notoriously hard to secure. Still using SMS-based two-factor authentication? It might be time to upgrade to more secure methods like authenticator apps or hardware keys. |
Disney Hacker Pleads Guilty to Massive Data Breach |
A 25-year-old man from California has admitted to hacking into Disney by tricking an employee into downloading fake AI art software. That tool was actually malware, which helped him steal over a terabyte of sensitive data, including unreleased projects and internal Slack messages. He pretended to be a hacktivist and leaked the data after failing to extort the company.
This is a reminder that not all threats come through phishing emails. Downloaded apps can be just as dangerous. Vet tools carefully before hitting install. |
|
|
-
Take control of credentials before attackers do. Keeper Security’s encrypted vault makes it easy to manage passwords, secrets, and access controls—whether securing a small team or scaling across an enterprise.
-
Standardize how your network runs with one easy policy. TechRepublic's ready-made DNS and DHCP usage policy helps IT teams tighten internal controls, avoid misconfigurations, and stay audit-ready.
|
🛡️ This section contains sponsored cybersecurity insights. |
|
|
Skip the Text Message, Save Your Account |
Cybercriminals are now selling SS7 exploits that let them intercept SMS messages—including those one-time codes you rely on for two-factor authentication. If your login depends on a text message, you could be one breach away from giving attackers a way in. |
Better ways to secure your logins: |
-
Use app-based authenticators: Tools like Authy or Google Authenticator generate codes locally, keeping them out of reach of network-based attacks.
- Go with hardware keys for high-value accounts: Devices like YubiKey offer physical protection that can’t be cloned or intercepted.
-
Add a carrier-level PIN: A simple PIN or password with your mobile provider helps defend against SIM swapping.
- Enable login alerts: Most platforms let you turn on notifications for unfamiliar sign-ins. Use them as an early warning system.
|
Switching your 2FA method might take a few minutes, but it’s one of the fastest ways to shut down a popular attack route. |
|
|
| Secure Links: The Must-Reads |
|
|
| Secure Links: The Must-Reads |
| |
Akamai and P3M Join Forces to Protect UK’s Defense Networks |
Akamai is teaming up with consulting firm P3M to roll out zero-trust identity and access systems for the UK’s government and defense supply chain. The goal is to lock down who can access what while verifying them every step of the way. With global threats rising, this partnership aims to keep sensitive systems safer from intrusions. |
Working with high-stakes data or suppliers? Zero Trust isn't a buzzword—it’s becoming a baseline. |
Cloudflare Steps Up Cyber Defense for Banks and Financial Orgs |
Cloudflare has joined FS-ISAC’s Critical Providers Program to help financial institutions detect and respond to cyber threats faster. By sharing real-time threat data across a global network, Cloudflare hopes to give banks and credit unions a stronger early-warning system.
Stronger intel sharing means faster reactions—and fewer nasty surprises for customers. | |
|
|
Leon Yen is a cybersecurity expert and seasoned tech journalist with over a decade of experience, including founding a cyber risk startup and leading industry-focused research and reporting. |
|
|
|
Liz Ticong is a tech writer specializing in AI and software tools, known for turning complex topics into clear, actionable insights through hands-on testing and analysis. |
|
|
We're looking for talented writers to help shape Cybersecurity Insider. If you're passionate about cyber security, apply to join our team! |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|