Good day, Digital Defenders! 🛡️ |
Today’s headlines bring AI-powered breakthroughs, large-scale takedowns, and cloud security red flags. Whether it’s RSA revelations or phishing fallout, we’ve got you covered with the latest intel. |
|
|
Here’s what you need to know: |
-
RSA 2025 Spotlights AI, Identity, and Unity as the Future of Cyber Defense
- FBI Exposes 42,000 Phishing Domains from Major Global PhaaS Operation
- ‘Shadow Roles’ in AWS Pose Critical Risk to Cloud Security, Researchers Warn
- Ascension Notifies Patients After Data Theft Involving Business Partner
|
|
|
RSA Conference 2025: AI and the Future of Cyber Defense |
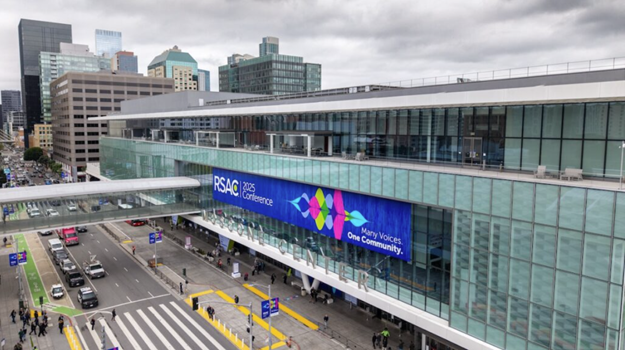
RSA Conference 2025 brought the cybersecurity world together in San Francisco with a clear message: collaboration and innovation are critical in staying ahead of evolving threats. |
Source: securityweek.com. |
This year’s theme—”Many Voices. One Community.”—highlighted the importance of uniting IT, security teams, and underrepresented voices to tackle systemic challenges like the "Security Poverty Line." The event showcased a new era of intelligent, adaptive cyber defense, from AI-powered security agents and identity vulnerability tools to crowdsourced red teaming and compliance automation.
Whether you’re a practitioner, strategist, or decision-maker, these insights can help you prepare for what’s next. |
FBI Releases 42,000 Phishing Domains Linked to Major Phishing Platform LabHost |
The FBI has released a list of 42,000 phishing domains associated with LabHost, a prominent phishing-as-a-service (PhaaS) platform dismantled in April 2024. The PhaaS outfit sold phishing kits targeting U.S. and Canadian banks, had over 10,000 customers globally, and was responsible for stealing over 1 million user credentials and 500,000 credit card records.
Cybersecurity teams can use the domain list to block potential future attacks, investigate past breaches, and improve phishing detection models. |
Anthropic's Claude AI Exploited to Run 100+ Fake Political Personas |
Anthropic revealed that unknown actors exploited its Claude AI chatbot in a covert campaign using over 100 fake personas on Facebook and X to interact with tens of thousands of real users, influencing geopolitical discourse related to Europe, Iran, the U.A.E., and Kenya.
The campaign highlights the growing risk of AI tools being misused to manipulate global political narratives at scale. |
|
|
Severe Vulnerability in Samsung MagicINFO Enables Unauthenticated System-Level Attacks |
A malicious automation script from Mora_001. Source: http://forescout.com/blog/new-ransomware-operator-exploits-fortinet-vulnerability-duo/. |
The flaw (CVE-2024-7399), rated 9.8 on the CVSS scale, stems from improper validation of user-supplied paths in file operations, enabling path traversal and arbitrary file writes. Affected versions include MagicINFO 9 Server releases before 21.1050. Users are strongly advised to apply the patch provided by Samsung. |
AWS Default Configs Expose Cloud Environments to Critical Privilege Escalation Risks |
Security researchers at Aqua Security have uncovered a critical AWS vulnerability tied to default service configurations that automatically deploy overly permissive IAM roles. These “shadow roles” in AWS services like SageMaker, Glue, and EMR often include AmazonS3FullAccess, making them highly exploitable for privilege escalation and cross-service attacks.
AWS users should regularly audit their roles and tighten broad permissions, especially S3 access, to prevent the hidden exposure of critical services. |
Ascension Healthcare Notifies Patients of Data Theft Affecting Personal, Health Information |
Ascension, one of the largest private healthcare systems in the U.S., has alerted patients that their personal and health information was stolen in a cyber attack involving a former business partner. The breach, discovered on Dec. 5, 2024, prompted an immediate investigation.
Affected individuals can enroll in two years of free identity monitoring services (courtesy of Ascension) to help detect and respond to potential fraud or identity theft. |
|
|
-
The right cybersecurity software can mean the difference between seamless operations and a devastating breach — find the best digital protection for your business in this guide.
-
See how organizations use NordLayer’s business-grade VPN to secure operations, ensure compliance, and integrate seamlessly with platforms like Azure, Google Workspace, and AWS.
-
Discover how a zero-trust cybersecurity approach strengthens IT infrastructure and prevents data breaches in this insightful article.
|
🛡️ This section contains sponsored cybersecurity insights. | |
|
Applying the CIA Triad to Improve Security |
The CIA Triad—Confidentiality, Integrity, and Availability—is a foundational security model that guides organizations in protecting data and systems from cyber threats and operational failures. These principles ensure sensitive information remains private, accurate, and accessible to authorized users. |
Source: cybersecuritynews.com. |
Although the CIA model is widely used in enterprise security, individual users can also apply its principles to strengthen their own cybersecurity. |
Here are some cybersecurity tips based on the CIA Triad: |
-
Confidentiality: Encrypt data, use MFA, restrict access, train against phishing, and audit regularly.
- Integrity: Apply hashing/signatures, run audits, patch systems, and use backups and version control.
- Availability: Ensure redundancy, filter traffic, test recovery plans, and maintain systems.
|
When implemented effectively, the CIA Triad forms the backbone of a strong cybersecurity strategy, helping to reduce risks from malicious attacks and accidental breaches. Be sure to revisit these principles regularly to stay resilient and secure. |
|
|
|
| Secure Links: The Must-Reads |
|
|
| Secure Links: The Must-Reads |
| |
Top Digital Forensics Tools: Features, Use Cases, and Expert Analysis |
Digital forensics tools assist businesses and legal teams uncover evidence related to security breaches, data privacy incidents, and legal disputes. Equipped with features like data extraction, anomaly detection, and detailed reporting, they sift through vast amounts of data to find hard-to-reach information. |
Top Open-Source Vulnerability Scanners for Uncovering Security Flaws |
Open-source vulnerability scanners are powerful tools for detecting security gaps like missing patches and misconfigurations, offering transparency and free access to robust features. This guide highlights the top scanners and provides advice for selecting the right tool for your security needs. |
|
|
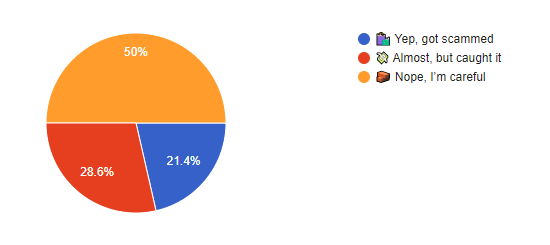
Security Question of the Week: Results |
Have you ever had your info stolen or almost stolen after shopping online? | Share your thoughts in our weekly poll—new every Monday! |
|
|
| Leon Yen is a cybersecurity expert and seasoned tech journalist with over a decade of experience, including founding a cyber risk startup and leading industry-focused research and reporting. |
|
|
|
Liz Ticong is a tech writer specializing in AI and software tools, known for turning complex topics into clear, actionable insights through hands-on testing and analysis. |
|
|
We're looking for talented writers to help shape Cybersecurity Insider. If you're passionate about cyber security, apply to join our team! |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|