Eyes up, Digital Defenders! 🛡️ |
Being big doesn’t make you safe—just a bigger target. NVIDIA’s latest vulnerabilities, bugs in Apple’s AirPlay, and misconfigured Git repos are just the latest reminders that everyone is a target: enterprises, developers, even casual users. Let’s drive in. |
|
| Here’s what you need to know: |
-
NVIDIA Riva Vulnerabilities Put AI Speech Tools at Risk
- Critical AirPlay Flaws Leave Apple Devices Open to Remote Exploits
- WhatsApp Enhances Privacy with New AI Feature for Secure Message Processing
- PurpleHaze Cyber Group Targets Leading Cybersecurity Firm
|
|
|
NVIDIA Riva Flaw Exposes AI Speech and Translation Services to Hackers |
Image source: cybersecuritynews.com. |
These flaws, caused by misconfigured cloud deployments, could let attackers bypass authentication, hijack GPU resources, steal proprietary AI models, or launch denial-of-service attacks.
Riva admins should review their configurations for exposure risks, update to the latest framework version, and follow NVIDIA's security best practices. |
AirPlay Attacked: Apple Scrambles to Patch 23 Critical Flaws |
A set of 23 critical vulnerabilities in Apple’s AirPlay protocol exposes devices to remote code execution, man-in-the-middle attacks, and sensitive data leaks. Discovered by Oligo Security, these flaws can be exploited on local networks, allowing attackers to hijack devices and spread infections.
Apple has released patches for iPhones, iPads, Macs, and Vision Pro. However, unpatched devices remain at risk, so users are advised to apply the fixes immediately. |
WhatsApp Unveils Privacy-First AI with 'Private Processing' |
WhatsApp introduced a new privacy-focused AI feature called “Private Processing,” designed to offer powerful AI capabilities like message summarization and editing while maintaining user privacy. The feature works by processing data within a secure, confidential virtual machine. This ensures no one, including Meta, can access the messages.
WhatsApp users should look for the new feature, which will be rolled out in the coming weeks. |
|
|
Grinex Crypto Exchange Suspected to Be Garantex in Disguise |
A new crypto exchange called Grinex is raising red flags after blockchain analysts at TRM Labs linked it to Garantex, a sanctioned Russian platform accused of laundering billions through ransomware and dark web markets. |
Image source: bleepingcomputer.com. |
Despite U.S. authorities seizing Garantex’s domain, the sanctioned exchange continues operating under the new Grinex name. Crypto traders are strongly advised to avoid Grinex, research exchanges thoroughly, and avoid platforms with unclear origins. |
Hackers Are Hunting Git Configs to Breach Clouds and Code |
Threat actors are ramping up internet-wide scans for exposed Git config files, which often contain sensitive access tokens and credentials tied to cloud services and source code repositories. According to GreyNoise, the spike in scanning activity hit nearly 4,800 unique IPs per day between April 20 and 21. This signals a coordinated effort to exploit misconfigured developer assets.
To mitigate this risk, developers should block access to .git/ directories, prevent exposure of hidden files, monitor for suspicious access, and promptly rotate any exposed credentials. |
Cybercriminal Group ‘PurpleHaze’ Probes SentinelOne and High-Value Targets |
SentinelOne has identified a China-associated threat group, “PurpleHaze,” attempting reconnaissance on its infrastructure and key clients. The group, loosely connected to the state-backed APT15, has previously targeted entities tied to South Asian governments using tools like the GoReShell backdoor and a covert ORB network.
SentinelOne customers are advised to stay on high alert, as not even cybersecurity companies are immune to threat actors. |
|
|
🛡️ This section contains sponsored cybersecurity insights. |
|
|
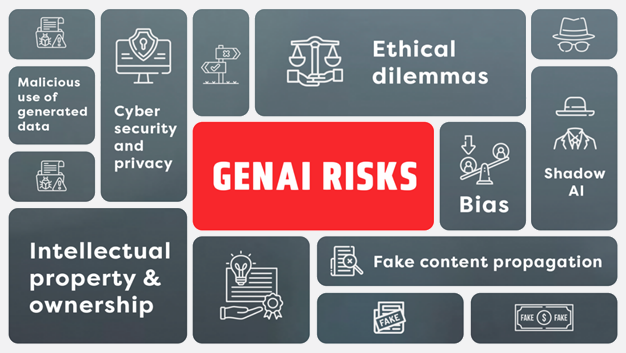
How to Mitigate GenAI Risks |
Generative AI (GenAI) is transforming how we work. But it’s also opening new doors for cybercriminals. To stay ahead, users and organizations must weigh the rewards of GenAI against its emerging security risks. | Image source: portal26.ai. |
To stay secure, you should move beyond traditional IT practices and adopt specialized tools and processes for AI environments. |
Here are some GenAI security best practices: |
- Inventory AI Components: Create an AI bill of materials (AI-BOM) to manage risks.
- Enforce Zero-Trust Security: Implement least-privilege access and continuous monitoring.
- Encrypt and Anonymize Data: Secure training and inference data with validation techniques.
- Map Compliance Regulations: Integrate relevant regulations like GDPR and the EU AI Act.
- Develop Response Plans: Create AI-specific incident playbooks and automate breach detection.
- Implement AI Security Tools: Use AI-SPM for continuous monitoring and automated risk mitigation.
-
Adopt Security Frameworks: Follow OWASP, NIST, and Gartner guidelines for security strategy.
|
These tips provide a solid foundation for securing your GenAI tools and processes, but your efforts shouldn’t stop here. By continuing to invest in AI-specific controls and fostering awareness, you can unlock GenAI's full potential while safeguarding safety and trust.
|
|
|
Semperis has published a new report grading global organizations on cyber incident response.
The State of Enterprise Cyber Crisis Readiness found that 96% of organizations have a cyber crisis response plan, yet high-impact cyber incidents still stopped critical business functions in the past year for 71%, and 36% suffered multiple major events. |
|
|
| Secure Links: The Must-Reads |
|
|
| Secure Links: The Must-Reads |
| |
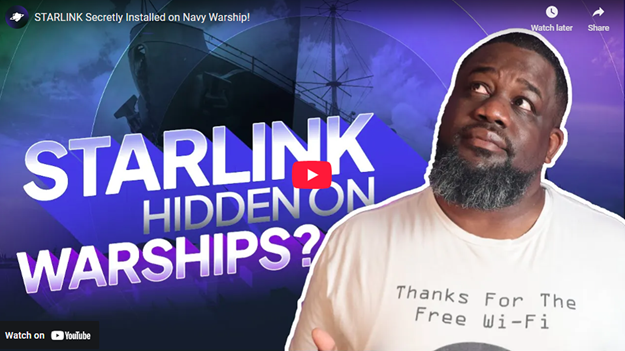
High-Speed Internet at Sea? The Navy’s Already There |
With Amazon's answer to Starlink launching this week, high-speed internet from anywhere is quickly becoming a reality—even in the most secure and critical locations. |
In this video, we break down how military officials set up Starlink on a Navy warship—not for mission-critical tasks, but to stream sports and Netflix at sea with high-speed internet. |
Securely Unlock Global Streaming on Your Amazon Fire TV Stick with the Right VPN |
Tired of hitting geo-blocks on your favorite shows? The best VPNs for Fire TV Stick let you bypass regional restrictions—all while adding a layer of privacy to your streaming activity. Check out our top five picks for 2025 and take your binge-watching to the next level. |
|
|
| Leon Yen is a cybersecurity expert and seasoned tech journalist with over a decade of experience, including founding a cyber risk startup and leading industry-focused research and reporting. |
|
|
|
Liz Ticong is a tech writer specializing in AI and software tools, known for turning complex topics into clear, actionable insights through hands-on testing and analysis. |
|
|
We're looking for talented writers to help shape Cybersecurity Insider. If you're passionate about cyber security, apply to join our team! |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|