Greetings, Digital Defenders! 🛡️ |
Cyber threats keep evolving, but so do defenses. From Google’s AI-powered security tools to new quantum encryption breakthroughs, today’s updates covers the key developments you need to stay protected. |
|
|
Here’s what you need to know: |
-
Google Unveils AI-Powered Security Tools, Expands Mandiant Integration
- Hackers Exploit Craft CMS Vulnerabilities, Breach Hundreds of Sites
- Hitachi Vantara Grapples with Ransomware as Servers Go Offline
- CISA Warns of Active Attacks on Broadcom and Commvault Systems
|
|
|
Google Deepens Mandiant Integration and Launches New AI Agents |
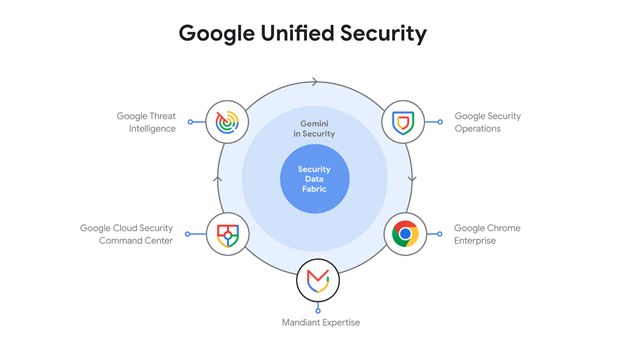
Google Cloud announced an expansion of its security offerings with new AI agents and deeper Mandiant integration into Google Unified Security. Introduced at RSA Conference 2025, the updates include tools for rule creation, incident response, and malware analysis, alongside composite detections that help analysts link complex threats. |
Google Unified Security. Source: google.com. |
The moves highlight Google's focus on embedding agentic AI into cybersecurity operations, a shift that could help organizations like yours catch sophisticated threats sooner and strengthen incident response. |
Critical Craft CMS Vulnerabilities Exploited: Over 300 Servers Breached |
Cybersecurity experts are sounding the alarm after attackers exploited two critical Craft CMS vulnerabilities—CVE-2024-58136 and CVE-2025-32432—leading to breaches of over 300 servers. Discovered by Orange Cyberdefense, the flaws allow hackers to upload malicious files and gain unauthorized access across Craft CMS versions 3.x to 5.x.
Craft CMS users are advised to patch their instance and review system logs for suspicious activity. |
Hitachi Vantara Hit by Ransomware Attack, Shuts Down Servers for Containment |
Hitachi Vantara confirmed a ransomware attack that disrupted some of its systems. The company swiftly activated its incident response protocols, took servers offline to contain the breach, and is working with third-party experts to investigate and restore operations securely.
Experts advise organizations to review their ransomware defenses and ensure incident response plans are current. |
|
|
CISA Flags Active Exploits in Broadcom Brocade Fabric OS and Commvault Web Server |
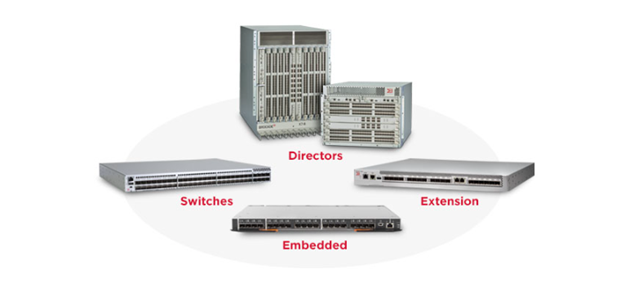
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added two high-severity vulnerabilities in Broadcom’s Brocade Fabric OS and the Commvault Web Server to its Known Exploited Vulnerabilities (KEV) catalog, citing active exploitation. |
Broadcom devices running Brocade Fabric OS. Source: broadcom.com. |
The flaws could allow attackers to gain root privileges or execute web shells if they possess valid user credentials, posing serious risks to affected systems. As a result, organizations are strongly urged to immediately apply available patches. |
Critical SEIKO EPSON Printer Driver Flaw Enables Windows Attacks |
A critical vulnerability in SEIKO EPSON printer drivers for Windows allows attackers to execute arbitrary code with SYSTEM-level privileges via DLL hijacking. The flaw stems from improper access permission settings and requires user interaction to exploit. If successful, attackers could fully compromise targeted systems, access sensitive data, or establish long-term persistence.
Organizations using EPSON drivers should immediately apply updates, restrict directory permissions, and monitor systems for signs of DLL hijacking attempts. |
Kali Linux Users Urged to Install New Repo Signing Key to Prevent Update Failures |
Offensive Security (Offsec) is warning Kali Linux users to manually install a new repository signing key after it lost access to the old one, risking update failures across all systems. Users relying on the old key will encounter signature verification errors when attempting updates.
OffSec froze the Kali repository on Feb. 18 to minimize disruption but plans to unfreeze it soon. Therefore, users should manually install the new key to maintain update functionality. |
|
|
🛡️ This section contains sponsored cybersecurity insights. | |
|
Smart Toys Require Smart Security |
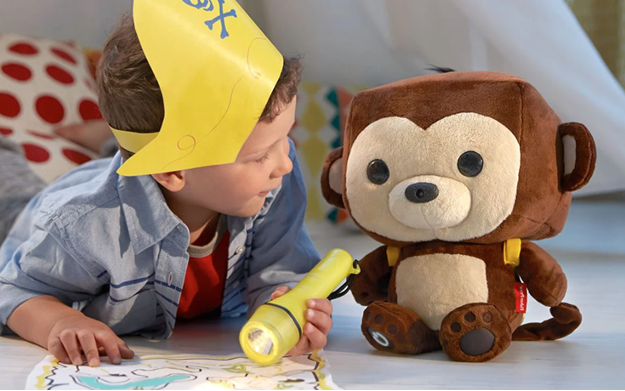
This Fisher Price Smart Toy Bear enabled the hacking of kids’ biological data. Source: telegraph.co.uk. |
If not properly secured, smart toys can become easy targets for hackers, exposing home networks and enabling active surveillance of your family.
|
Here are some tips for making smart toys safer for kids: |
- Change default passwords to strong, unique ones immediately after setup.
- Enable parental controls to manage communication, content, and spending.
-
Secure your home network with encryption and consider a separate IoT network.
- Check for marks indicating compliance with US ASTM F963 safety requirements and upcoming EU cybersecurity standards.
|
From hijacked cameras to creepy in-app messaging, recent smart toy cyber incidents have shown how easily these devices can be turned against you. The risks are real, and high-profile breaches show these toys need thoughtful oversight. |
|
|
|
| Secure Links: The Must-Reads |
|
|
| Secure Links: The Must-Reads |
| |
Selecting the Top Threat Intelligence Platform |
Threat intelligence platforms (TIPs) play a critical role in modern cybersecurity by consolidating external threat feeds and internal logs into actionable, prioritized alerts. In this guide, we assess the seven leading TIPs on the market—comparing features, pricing, and key capabilities—to help you find the best fit for your organization’s security needs.
|
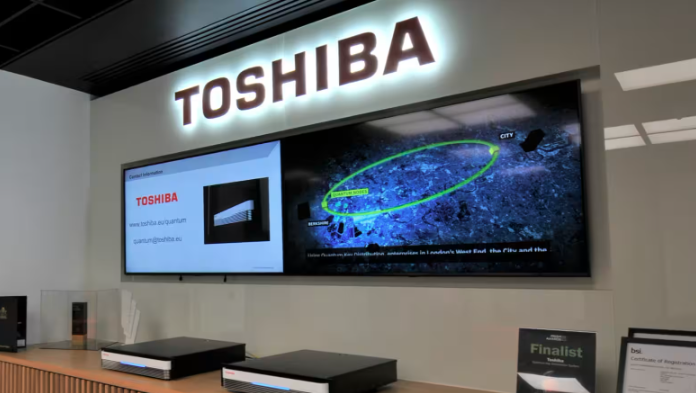
Toshiba Europe Makes Quantum Encryption Breakthrough |
In a groundbreaking experiment, Toshiba Europe has set a new distance record for quantum encryption without the need for cryogenic technology. |
Toshiba Europe’s Quantum Research Center. Source: nikkei.com. |
|
|
| Leon Yen is a cybersecurity expert and seasoned tech journalist with over a decade of experience, including founding a cyber risk startup and leading industry-focused research and reporting. |
|
|
|
Liz Ticong is a tech writer specializing in AI and software tools, known for turning complex topics into clear, actionable insights through hands-on testing and analysis. |
|
|
We're looking for talented writers to help shape Cybersecurity Insider. If you're passionate about cyber security, apply to join our team! |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|