Welcome, Digital Defenders! 🛡️ |
Cyber threats are evolving faster than ever, and no one is immune. From retail giants to software powerhouses, attackers are exploiting every vulnerability they can find. In a world where a single malicious command can brick your iPhone or block critical Windows updates, staying informed isn't just important—it's survival. |
|
|
Here’s what you need to know: |
-
Verizon DBIR: Unpatched VPNs and Edge Devices Drive 34% Exploit Surge
- Windows Fix Creates New Risk: 'Inetpub' Folder Can Block Future Updates
- Active Exploits of Critical SAP NetWeaver Zero-Day Prompt Urgent Patching
- iOS Vulnerability Exploit Bricks iPhones With One Line of Code
|
|
|
Verizon DBIR: VPN and Edge Device Vulnerabilities Contributed to 34% Rise in Exploitation |
The latest Verizon DBIR reveals that only 54% of vulnerabilities in VPNs and internet-facing devices were fully patched in 2024, with devices from Ivanti, Fortinet, SonicWall, and Citrix among the most exploited. This led to a 34% rise in vulnerability exploitation, making it the second-most common breach method after stolen credentials.
|
Source: linkedin.com/pulse/verizon-2025-data-breach-investigations-dbir-report-4pwfe/. |
Organizations should prioritize timely patching and strengthen edge device security to mitigate these risks. |
Fake WooCommerce Patch Hijacks WordPress Sites in Phishing Campaign |
A widespread phishing campaign is targeting WooCommerce administrators with fraudulent security alerts, urging them to install a "critical patch.” Instead of protecting their WordPress sites, the downloaded plugin installs a backdoor using a hidden admin account, deploying web shell payloads, and establishing persistent access.
WooCommerce users should install the patch immediately and ensure all their WordPress plugins are up-to-date. |
Windows Security Fix Creates New Risk: 'Inetpub' Folder Can Block Future Updates |
|
|
A recent Windows security update (CVE-2025-21204) meant to fix a privilege escalation flaw creates a new “inetpub” folder—even on systems without IIS installed. While Microsoft advises against deleting the folder, cybersecurity expert Kevin Beaumont explained that attackers can manipulate it to block future Windows updates, posing a new risk for users and IT admins.
The severity of the security risk remains unclear, as Microsoft has declined to release an immediate fix despite Beaumont’s findings. Users are advised to closely monitor updates regarding the issue via Microsoft’s website. |
|
|
Marks & Spencer Suspends Online Orders Amid Ongoing Cyber Attack Recovery |
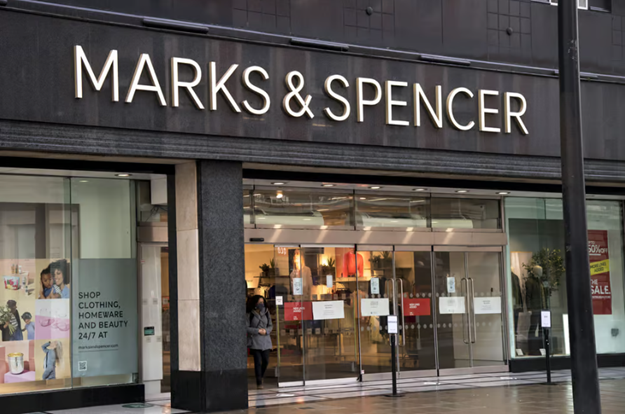
British retail giant Marks & Spencer (M&S), which we flagged for cybersecurity concerns in our previous edition, has paused online orders to recover from a recently disclosed cyberattack. The company confirmed that while customers can still browse products, these online stores will hold all orders until further notice. Physical stores remain open while the attack is being investigated.
|
Retail cyberattacks like this are a reminder to stay vigilant when shopping online. Always monitor your accounts and use secure payment methods. |
SAP NetWeaver Zero-Day Exploited in Active Attacks |
SAP is urging NetWeaver users to apply an out-of-band patch for a critical zero-day vulnerability (CVE-2025-31324) actively exploited by threat actors. The Visual Composer flaw allows unauthenticated attackers to upload arbitrary files, leading to full remote code execution and total system compromise.
Onapsis Research Labs, which discovered the zero-day, will hold a briefing on Tuesday, April 29, during which they will share their findings and launch an open-source SAP scanner. |
Critical iOS Vulnerability Disables Devices with One Line of Code |
App developer Guilherme Rambo has discovered a critical iOS vulnerability that allows malicious applications to permanently disable iPhones with just a single line of code.
The flaw exploits Darwin notifications, a low-level messaging system within iOS’s CoreOS layer, which allows apps to send system-level notifications without special privileges. By triggering the “Restore in Progress” state, the device enters an endless reboot cycle, effectively "bricking" it and requiring a full system restore to fix.
To fix the vulnerability, iOS users should update their devices to version 18.3. Apple has yet to publish the CVE and official note regarding the vulnerability. |
|
|
🛡️ This section contains sponsored cybersecurity insights. |
|
|
Make Your Car Less Hackable |
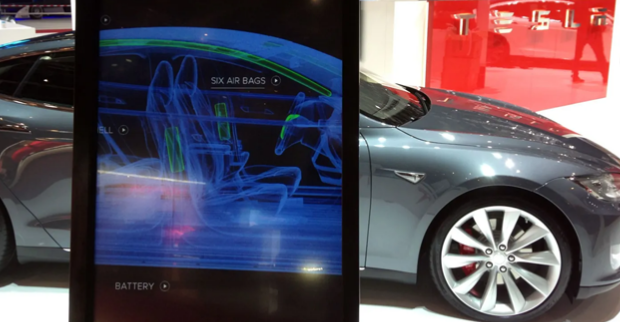
Car hacking is a growing risk, particularly for vehicles with advanced driver assistance systems—electric or not. Most personal auto policies don't directly cover hacking, though related damages like theft or collisions may be. Commercial policies may offer broader protection, but insurers could soon require basic cybersecurity measures from drivers. |
Here’s how you can make your car less hackable: |
- Update software: Check regularly for manufacturer patches or recalls.
- Use a Faraday bag: Block key fob signals when not driving.
- Vet your mechanic: Research before repairs to avoid tampering.
- Cover your VIN: Hide it to prevent unauthorized access.
-
Don’t save GPS addresses: Avoid storing personal locations.
- Use strong passwords: Protect connected devices with secure passwords.
- Unplug OBD-II devices: Disconnect when parked; reconnect before driving.
|
As cars evolve into rolling computers, the line between automotive and cybersecurity continues to blur. Protecting your vehicle now demands the same vigilance and proactive approach as safeguarding your digital life. For cyber-aware drivers, taking vehicle security seriously isn't just smart—it's essential. |
|
|
Semperis has published a new report grading global organizations on cyber incident response.
The State of Enterprise Cyber Crisis Readiness found that 96% of organizations have a cyber crisis response plan, yet high-impact cyber incidents still stopped critical business functions in the past year for 71%, and 36% suffered multiple major events. |
|
|
| Secure Links: The Must-Reads |
|
|
| Secure Links: The Must-Reads |
| |
Securing Enterprise Networks in the Age of Generative AI |
Enterprise AI adoption is in overdrive, with large organizations deploying GenAI across data centers, campuses, branches, clouds, and remote locations. And while over 80% of businesses are expected to use GenAI by 2026, less than half are prepared for the cybersecurity challenges, according to McKinsey.
Find out how AI-based network architectures for AI-ready enterprises can help mitigate these risks. |
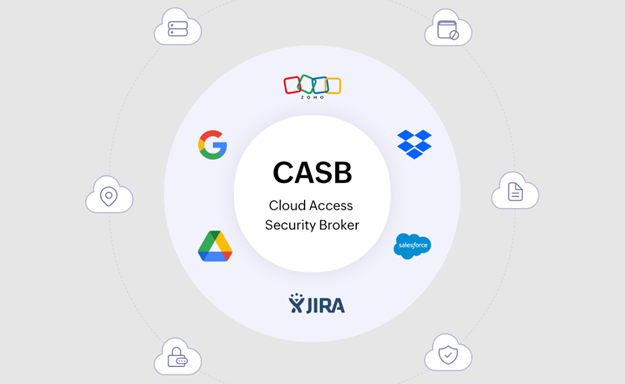
Modern Cloud Security Demands CASBs—So Don’t Be a ‘CASNOT’ |
Without the right protection, hackers can easily exploit gaps in your cloud environment. A cloud access security broker (CASB) helps secure data and enforce policies across cloud, edge, and mobile services.
|
|
|
|
Leon Yen is a cybersecurity expert and seasoned tech journalist with over a decade of experience, including founding a cyber risk startup and leading industry-focused research and reporting. |
|
|
|
Liz Ticong is a tech writer specializing in AI and software tools, known for turning complex topics into clear, actionable insights through hands-on testing and analysis. |
|
|
We're looking for talented writers to help shape Cybersecurity Insider. If you're passionate about cyber security, apply to join our team! |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|