Brace yourselves, Digital Defenders! 🛡️ |
Crypto prices are rising, and so are cyber threats. From crypto-focused exploits to a new Google Cloud vulnerability, today's updates remind us that vigilance is key. Plus, we’ve got a quick tip to help keep your Bluetooth devices safe from hackers. | |
|
Here’s what you need to know: |
-
Malware Abuses Docker and Web3 Platform Teneo to Farm Crypto Rewards
- Google Cloud Platform Flaw Allows Privilege Escalation via Default Service Account
- Malicious Code in Ripple Library Exposes XRP Wallet Keys to Theft
- ‘Cookie Bite’ Exploit Bypasses MFA to Hijack Microsoft 365 via Entra ID Cookies
|
|
| New Malware Campaign Hijacks Docker to Exploit Web3 for Crypto Mining |
Researchers have uncovered a malware campaign targeting Docker environments to exploit Teneo, a Web3 platform that rewards users for scraping social media content. Instead of deploying typical crypto miners, the malware launches a container that connects to Teneo’s network, harvesting social posts to earn $TENEO Tokens. |
If you’re running Docker, be sure to monitor container activity regularly, restrict access to trusted images, and watch for unusual outbound traffic. |
ConfusedComposer Flaw in Google Cloud Platform Enables Privilege Escalation via Cloud Composer |
Tenable security researchers discovered a privilege escalation vulnerability in Google Cloud Platform (GCP) that could allow users with permission to update Cloud Composer environments. By exploiting the default Cloud Build service account, which holds broader permissions across services like Cloud Storage and Artifact Registry, users could elevate their access.
Although the flaw has since been patched, organizations should review IAM roles and limit sensitive permissions to reduce exposure to similar risks. |
Ripple JavaScript Library xrpl.js Compromised to Steal XRP Wallet Keys |
Cyberattackers compromised Ripple’s recommended JavaScript library, xrpl.js, injecting malicious code into multiple versions to steal wallet seeds and private keys. The tainted packages redirected sensitive data to an attacker-controlled server, enabling theft of XRP funds. The impact could be significant, with over 140,000 downloads in the past week.
Users should immediately upgrade to the clean 4.2.5 version and rotate any exposed credentials. |
|
|
‘Cookie Bite’ Exploit Bypasses MFA to Hijack Microsoft 365 Sessions via Entra ID Cookies |
The proof-of-concept attack enables persistent access to services like Outlook and Teams, allowing hackers to conduct recon, escalate privileges, and potentially launch broader attacks. Organizations are urged to monitor session activity and review browser authentication token handling. |
Cyberattack Forces Texas City to Take Systems Offline, Disrupts Services |
The City of Abilene, Texas, shut down parts of its internal network following an extensive cyberattack. In response to unresponsive servers, IT staff disconnected affected systems and brought in cybersecurity experts to investigate. While emergency services remain operational, card payment systems at government offices are down. Residents are encouraged to use cash, checks, or online payments.
The city is actively monitoring for suspicious activity and working to restore normal operations. |
Active! Mail Zero-Day RCE Flaw Exploited in Attacks on Major Japanese Organizations |
A zero-day remote code execution vulnerability in Active! Mail, a web-based email client popular in Japanese enterprise environments, is being actively exploited in targeted attacks. The flaw allows attackers to execute malicious code remotely, and it is used by prominent corporations, universities, and government agencies in Japan.
Organizations using Active! Mail should apply updates immediately and monitor systems for signs of compromise. |
|
|
-
Take control of your online security with Keeper Security, the trusted leader in password management. New users get 30% off any 1-year plan.
-
Sticky Password is a powerful, all-in-one solution for generating strong passwords. Get 87% off the Premium Lifetime Subscription 2-Account Bundle.
|
🛡️ This section contains sponsored cybersecurity insights. |
|
|
How to Avoid the Bluetooth Blues |
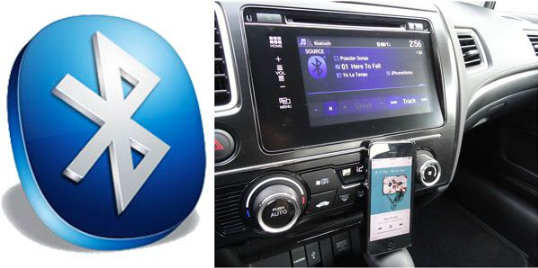
Those earbuds might sound great, but are they opening a door for hackers? Bluetooth is ubiquitous, convenient, and unfortunately risky—especially when used in public or shared spaces. Common threats include data leaks from rental car syncs, eavesdropping via shared speakers, and unauthorized access through insecure pairings.
|
Source: selectcarleasing.co.uk. |
Bluetooth pop-ups, geolocation tracking in shared headphones, and devices overwriting previous connections can also lead to privacy breaches. |
Here’s how you can protect yourself from Bluetooth-related security risks: |
- Regularly delete unused paired devices.
- Use PINs when pairing input devices.
- Turn off Bluetooth when not in use.
- Avoid connecting to unknown devices.
- Unpair and clear data from rental cars or shared devices.
|
By staying alert and practicing good Bluetooth hygiene, you can safeguard your personal and business data from potential Bluetooth-related threats. |
|
|
We’ve saved you a seat for Cisco Secure Access Live Demo
|
Hi there, Secure access, simplified. Join Cisco’s Secure Access live demo on May 21 to learn how to protect users anywhere — and get a free pair of Cisco socks for attending the session! |
*Offer is only available in the US while supplies last. |
|
|
|
| Secure Links: The Must-Reads |
|
|
| Secure Links: The Must-Reads |
| |
Top Secure Cloud Storage Solutions for Privacy & Protection in 2025 |
Safeguarding your data in the cloud has never been more critical, but not every storage solution is up to par. We’ve evaluated the leading solutions focusing on privacy, encryption, and advanced protection features. Explore the most secure cloud storage options for 2025 and select the best one to keep your data safe. |
Video: Top 5 Data Management Platforms
|
Get the insights you need to choose the right platform and stay on top of your data management game |
|
|
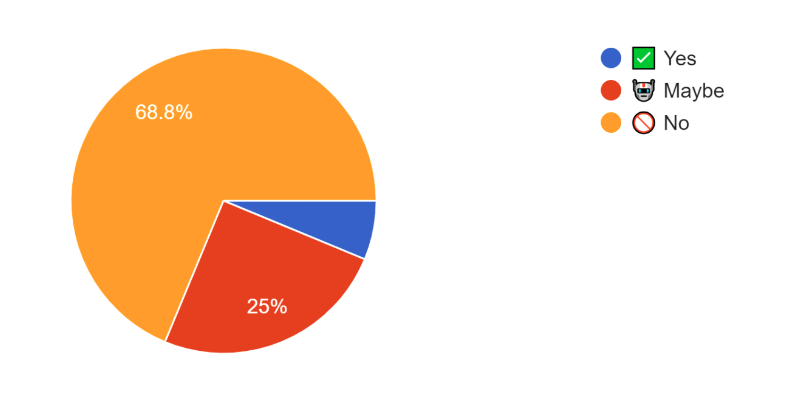
Security Question of the Week: Results |
Would you trust AI to write your company's code? | Share your thoughts in our weekly poll—new every Monday! |
|
|
| Leon Yen is a cybersecurity expert and seasoned tech journalist with over a decade of experience, including founding a cyber risk startup and leading industry-focused research and reporting. |
|
|
|
Liz Ticong is a tech writer specializing in AI and software tools, known for turning complex topics into clear, actionable insights through hands-on testing and analysis. |
|
|
We're looking for talented writers to help shape Cybersecurity Insider. If you're passionate about cyber security, apply to join our team! |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|