Greetings, Digital Defenders! 🛡️ |
This week’s developments reveal just how borderless digital risks have become. Hackers breached South Korea’s largest mobile carrier, compromising sensitive data, while a Russian hosting firm actively facilitated a wave of global cyberattacks. Malicious actors don’t care about geography, politics, or economics—everyone is a potential target. |
|
|
Here’s what you need to know: |
-
Microsoft Reports Progress on Secure Future Initiative, Boosts Identity Security and Cloud Protections
- Fog Ransomware Shifts to Phishing Tactics with DOGE-Themed Ransom Notes
- SK Telecom Investigates Cyberattack After Partial USIM Data Leak
- Billbug Group Targets Southeast Asia in Ongoing Espionage Campaign
|
|
|
Microsoft SFI Update: Cloud Security Tightened, Millions of Dormant Azure Tenants Purged |
Microsoft cited major cybersecurity strides in its Secure Future Initiative (SFI) progress report, including moving all key identity tokens into hardware security modules or confidential VMs to prevent future breaches. The company also purged 6.3 million inactive Azure tenants, migrated most resources to Azure Resource Manager, and rolled out phishing-resistant MFA across internal accounts.
|
Launched in response to a major hack and a critical U.S. government report, the SFI has nearly completed five of its 28 goals, but Microsoft continues to face scrutiny over cloud security and patch reliability. |
Fog Ransomware Campaign Masquerades as DOGE in Phishing Attacks |
Trend Micro researchers warn that Fog ransomware attackers are now using DOGE-themed ransom notes to mock victims, offering free decryption if they spread the malware. Unlike past campaigns that used stolen VPN credentials, the latest attacks start with phishing emails containing a malicious "Pay Adjustment.zip" file that installs the ransomware when opened.
Users should avoid opening unexpected email attachments and verify the source before clicking on any files. |
Japan Links Surge in Hacked Trading Accounts to $700M in Fraudulent Trades |
Japan’s Financial Services Agency (FSA) has issued a warning after nearly $700 million in unauthorized trades were linked to a surge in hacked trading accounts since March. The breaches stem from stolen credentials via phishing websites and infostealer malware.
The Japan Securities Dealers Association (JSDA) also warned that cybercriminals are exploiting the crisis to launch more phishing attacks. They pose as official institutions to trick users into clicking on malicious links. |
|
|
SK Telecom Probes Hack Involving Partial Leak of USIM Customer Data |
SK Telecom reported a cyberattack that led to a partial leak of customer USIM data, traced to malicious code inserted by an unknown hacker. The company has since removed the code, isolated the affected system, and alerted the proper authorities. |
SK Telecom is offering free USIM protection while regulators review the incident and may issue corrective action. |
Security Researchers Link Russian Host Proton66 to Global Cyberattacks |
Trustwave SpiderLabs researchers have linked Russian hosting provider Proton66 to a wave of global cyberattacks involving ransomware, phishing, and credential brute-forcing. Known for offering “bulletproof hosting,” Proton66 enables criminal activity and has resurfaced under names like UNDERGROUND and BEARHOST. Users and organizations should monitor unusual network activity and keep systems patched to reduce exposure to such threats. |
Billbug/Lotus Panda Targets Southeast Asian Governments in Espionage Campaign |
The China-linked cyber espionage group Billbug, also known as Lotus Panda, has been tied to a series of attacks on Southeast Asian government and industry targets from August 2024 to February 2025. Victims include a government ministry, air traffic control, a telecom operator, a construction firm, and regional media and logistics organizations. Symantec says the group used custom tools in a campaign tied to a broader operation active since October 2023.
Users and organizations active in the region during this period should watch for unusual remote access attempts and ensure that their endpoint security is up to snuff. |
|
|
🛡️ This section contains sponsored cybersecurity insights. |
|
|
Small Businesses are Big Targets for Cyberattackers |
Cybercriminals are equal-opportunity exploiters—wherever there's an exposed vulnerability, a compromise is likely to go down, be it in a large enterprise or a small business.
However, small businesses are especially at risk because they have limited (or no) cybersecurity budgets. As a result, they should arm themselves with preventative know-how, especially if top-tier cybersecurity tools are out of reach. Here are some practical tips to protect your business: |
Small businesses can build a strong line of defense against cyber threats by understanding the risks and taking simple, proactive steps.
Remember—when it comes to security, even small actions can make a big difference. |
|
|
| Secure Links: The Must-Reads |
|
|
| Secure Links: The Must-Reads |
| |
Bitwarden vs. LastPass: Which Password Manager Should You Choose? |
Password security is more crucial than ever, but the abundance of available tools can feel overwhelming. Bitwarden and LastPass stand out among the top contenders for their strong password management features. This article can help you determine which of the two leading password managers best suits your specific password security needs. |
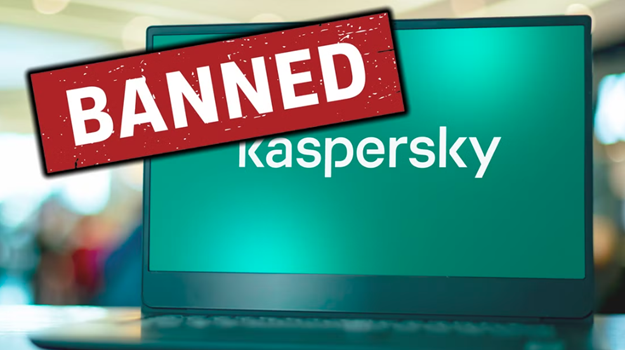
Still Using Kaspersky? Now’s the Time to Switch |
Once a leading name in endpoint security, Kaspersky was banned in the U.S. late last year over concerns about ties to the Russian government. If you’re still using it for endpoint protection, yesterday was the time to start exploring alternatives, especially since upgrades have been discontinued. |
Source: kaspersky-logo-on-laptop-with-banned-sign.jpg |
|
|
| Leon Yen is a cybersecurity expert and seasoned tech journalist with over a decade of experience, including founding a cyber risk startup and leading industry-focused research and reporting. |
|
|
|
Liz Ticong is a tech writer specializing in AI and software tools, known for turning complex topics into clear, actionable insights through hands-on testing and analysis. |
|
|
We're looking for talented writers to help shape Cybersecurity Insider. If you're passionate about cyber security, apply to join our team! |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|