Greetings, Digital Defenders! 🛡️ |
With half the week already behind us, it’s the perfect time to take stock of what’s unfolding across the cybersecurity landscape. From electric vehicle flaws to widespread data breaches impacting the public, today’s edition brings you critical updates and insights to stay informed this week. |
|
|
Here’s what you need to know: |
-
Prodaft Buys Access to Cybercrime Forums for Dark Web Intelligence
- Phishing Attacks Unleash ResolverRAT Malware on Healthcare Organizations
- Conduent Reports Data Theft in Cyberattack, Impacting Client Files
- Hertz Data Breach Exposes Customer Credit Card and Driver's License Info
|
|
|
Cybersecurity Firm Buys Dark Web Accounts to Monitor Cyber Criminals |
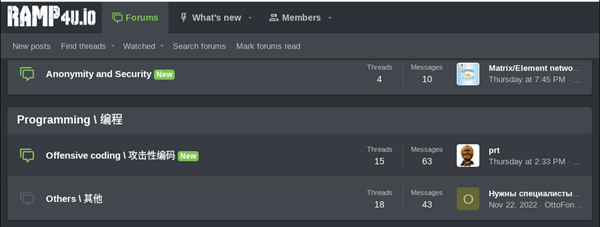
Threat intelligence firm Prodaft has adopted an unconventional approach to monitoring cybercriminal activities by purchasing accounts on dark web forums. The company’s SYS initiative involves buying vetted accounts from five known cybercrime forums: XSS, Exploit in, RAMP4U, Verified, and Breachforums. |
Prodaft is buying vetted accounts from RAMP4U. Source: resecurity.com. |
This strategy aims to gather insights into illicit cryptocurrency transactions and identify emerging threats within underground communities. |
Healthcare Organizations Targeted in ResolverRAT Malware Campaign |
A new malware campaign deploying ResolverRAT has been targeting healthcare organizations, aiming to exfiltrate sensitive patient data. The attackers use phishing emails to deliver the malware, establishing persistence and communicating with command-and-control servers to extract information.
If you work in healthcare, you’re an active target—be wary of phishing emails and avoid clicking links or downloading attachments from unknown sources. |
Nissan Leaf Hack Exposes Risks of Remote Vehicle Exploitation |
Security researchers have demonstrated vulnerabilities in the Nissan Leaf electric vehicle that could allow attackers to remotely spy on drivers and potentially take control of certain functions. The flaws highlight the growing concerns over the cybersecurity of connected cars and the need for robust protective measures.
Nissan Leaf owners should update their vehicle’s firmware and disable unnecessary remote features when not in use. |
|
|
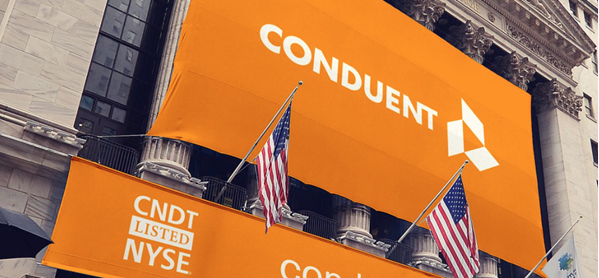
GovTech Firm Conduent Confirms Client Data Theft in January Cyberattack |
Conduent confirmed that a cyberattack in January led to the theft of files containing client information. The business services provider is collaborating with cybersecurity experts to assess the scope of the breach. It has notified affected clients while continuing its investigation. |
The breach serves as a stark reminder of the growing danger linked to third-party vulnerabilities. Before working with third-party vendors, you should assess supply chain risk and enforce strict data-sharing policies. |
Hertz Data Breach Exposes Customer Driver's License and Payment Info |
Hertz Global Holdings disclosed a data breach resulting from vulnerabilities in a third-party file transfer platform, Cleo Communications. The breach potentially exposed customers' contact details, credit card numbers, and driver's license information. Hertz emphasized that its internal systems were not compromised and has found no evidence of fraudulent use of the stolen data.
If you’ve recently rented a car from Hertz, be sure to monitor your credit reports closely for sudden activity or changes. |
Ransomware Attack Targets DaVita, Disrupts Operations but Patient Care Maintained |
Major U.S. dialysis provider DaVita reported a ransomware attack that encrypted parts of its network, causing operational disruptions. Despite the incident, the company continued to provide patient care services and implemented interim measures to restore affected systems. DaVita is working with cybersecurity experts and law enforcement to investigate the breach.
Patients and staff should remain vigilant for suspicious communications, as attackers may attempt to exploit stolen data for phishing. |
|
|
-
Simplify your IT operations with NinjaOne's Mobile Device Management. The solution allows you to manage, monitor, and secure all your organization's devices from a single, intuitive dashboard.
-
Struggling to enforce consistent DNS and DHCP rules across your organization? This ready-to-use DNS and DHCP Usage Policy helps you establish clear, effective guidelines that IT teams can implement right away.
|
🛡️ This section contains sponsored cybersecurity insights. |
|
|
We’ve saved you a seat for Cisco Secure Access Live Demo
|
|
|
Hi there,
Complicated. Challenging. Complex. Security leaders describe the current state of cybersecurity this way. Yet, security should be simple. Protect users as they access applications and resources and stop threats before they reach your users or network.
Join us on April 16 to discover a smarter way to manage access – from anything to anywhere – while protecting against savvy, sophisticated attackers. Webinar attendees will receive a gift of free Cisco socks as a thank you for joining us live!*
Cisco Secure Access, a Security Service Edge (SSE) solution, lowers risk in decentralized, hybrid work environments. It delivers secure access, comprehensive cloud-delivered security services, and centralized management for better protection against threats. | |
|
*Offer is only available in the US while supplies last. |
|
|
Bolster Your EV’s Cybersecurity Controls |
Lately, we’ve been reporting on a growing number of cybersecurity issues affecting electric vehicles. The truth is, many drivers have no idea just how vulnerable their EVs might be. Today’s connected cars are essentially rolling computers, making them prime targets for attackers. |
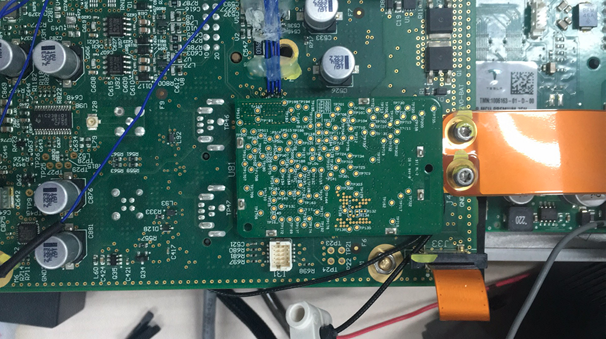
Tencent security researchers hacking a Tesla Model S wireless/Bluetooth module. Source: keenlab.tencent.com. |
Security often lags behind as automakers race to innovate with the latest bells and whistles, leaving critical systems at risk. If you think your EV is secure by default, it might be time for a closer look. |
Here Are Some Ways to Protect Yourself From EV Hacks: |
-
Use strong, unique passwords: Avoid personal info like birthdays. Opt for long, random codes, especially if your car uses a keypad entry system.
- Be cautious with public chargers: Stick to trusted brands and watch for fake interfaces that mimic legitimate companies to steal payment info.
-
Stay updated: Install official software updates when they’re available to patch vulnerabilities to protect your EV.
- Avoid third-party software: Only trust software from your vehicle’s manufacturer. Third-party tools can introduce serious security risks.
|
As electric vehicles become more common, the need for strong, built-in cybersecurity is becoming critical. But with most manufacturers still catching up, it’s up to EV owners to take proactive steps. |
|
|
| Secure Links: The Must-Reads |
|
|
| Secure Links: The Must-Reads |
| |
Mastering LastPass for Secure Password Management |
With long, complex passwords now the standard, remembering them all is unrealistic — making password managers like LastPass a must. This step-by-step guide covers everything you need to get started, from setup information to key features that streamline and secure your login experience. |
Top Intrusion Detection and Prevention Systems for 2025 |
Intrusion detection and prevention systems (IDPS) are like home alarm systems for your network, constantly monitoring for cyber break-ins. If you're connected to the internet, your systems are always in a bad neighborhood — and danger always lurks.
|
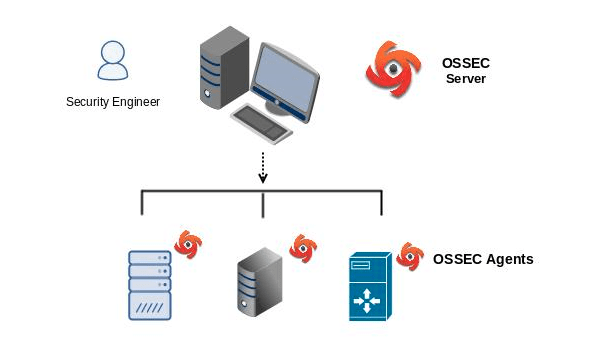
OSSEC architecture. Source: logz.io. |
|
|
| Leon Yen is a cybersecurity expert and seasoned tech journalist with over a decade of experience, including founding a cyber risk startup and leading industry-focused research and reporting. |
|
|
|
Liz Ticong is a tech writer specializing in AI and software tools, known for turning complex topics into clear, actionable insights through hands-on testing and analysis. |
|
|
We're looking for talented writers to help shape Cybersecurity Insider. If you're passionate about cyber security, apply to join our team! |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|