Happy Tuesday, Digital Defenders! 🛡️ |
The week’s in full swing, and so are the latest cyber threats and data breaches. Today's top stories spotlight what's being exploited, from brute-force attacks on Palo Alto gateways to critical flaws in WordPress and AI apps. Stay sharp, stay patched, and scroll on to secure your edge. |
|
|
Here’s what you need to know: |
-
Palo Alto Networks Warns of Brute-Force Attacks Targeting GlobalProtect Gateways
- 11 Vulnerabilities Discovered in Perplexity Chatbot's Android App
- Critical Vulnerability in OttoKit WordPress Plugin Under Active Exploitation
- Incomplete Patch in NVIDIA Toolkit Leaves Systems Vulnerable to Attackers
|
|
|
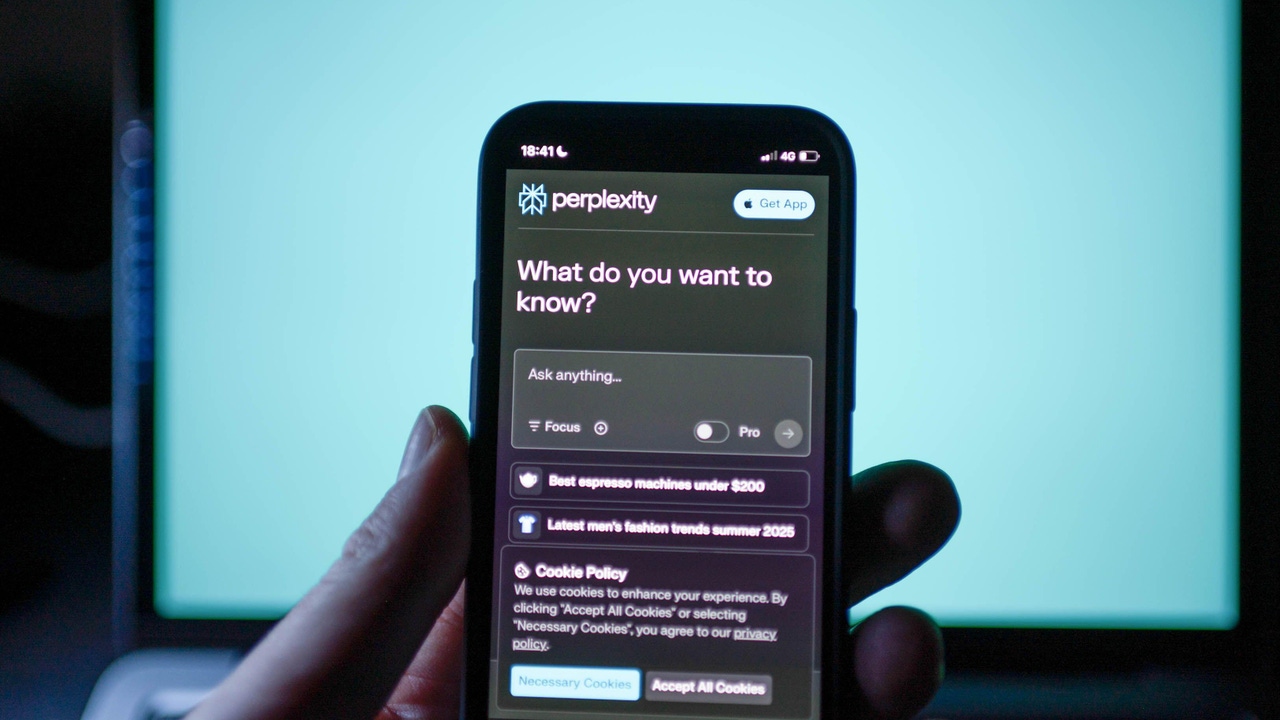
Numerous Vulnerabilities Discovered in Perplexity Chatbot's Android App |
The Perplexity AI Chatbot for Android. Source: darkreading.com. |
Perplexity Chatbot for Android users are advised to promptly update to the latest version to mitigate potential risks. |
Palo Alto Networks Warns of Brute-Force Attacks on GlobalProtect Gateways |
Palo Alto Networks has issued a warning about ongoing brute-force login attempts targeting its PAN-OS GlobalProtect gateways. The attacks, which began on March 17, peaked with activity from nearly 24,000 unique IP addresses before subsiding later in the month.
To mitigate potential risks, the company advises users to implement multi-factor authentication, update to the latest PAN-OS versions, and limit unnecessary internet exposure. |
Incomplete Patch in NVIDIA Toolkit Leaves Systems Vulnerable to Attacks |
An incomplete fix for a previously addressed vulnerability (CVE-2024-0132) in NVIDIA's Container Toolkit has been identified, leaving systems susceptible to container escape attacks. The flaw allows attackers with access to a container to execute arbitrary code on the host system.
Administrators should apply the latest patches and monitor container activities closely. |
|
|
Magento Breach Leaks CRM Data of 700K Users |
A threat actor known as "Satanic" has claimed responsibility for breaching Magento through a third-party integration, resulting in the leak of CRM data for over 700,000 users. The leaked information includes emails, phone numbers, and company details, posing significant risks for phishing and social engineering attacks.
Organizations using Magento are urged to review third-party integrations and enhance their security measures. |
Popular WordPress Plugin ‘OttoKit’ Being Actively Exploited |
A high-severity vulnerability (CVE-2025-3102) in the OttoKit WordPress plugin is being actively exploited, allowing attackers to create administrator accounts without proper authorization. The flaw stems from an authentication bypass issue due to improper handling of the 'secret_key' parameter.
Researchers caught the breach—but not before thousands of developers potentially fed their credentials straight to hackers. |
The Ottokit plugin. Source: wordpress.org. |
Website administrators are advised to update to version 1.0.79 immediately and audit user accounts for any unauthorized additions. |
Zero-Day Vulnerability in CentreStack Platform Exploited in the Wild |
Threat actors are actively exploiting a zero-day vulnerability in the CentreStack file-sharing platform. The flaw allows unauthorized access to sensitive files and could lead to data breaches. Administrators are urged to apply available patches and monitor systems for unusual activities. |
|
|
-
Want to stay ahead of hackers and lock down your digital defenses? Check out our top picks for the Best Vulnerability Management Software of 2025 roundup—because if you don’t discover your own security gaps, a cyberattacker surely will.
-
Ready to level up your skills? The Masters in Cyber Security Certification Bundle delivers expert training to help you outsmart even the most sophisticated cybercriminals—and gives you a competitive edge in a crowded cybersecurity job market.
|
🛡️ This section contains sponsored cybersecurity insights. |
|
|
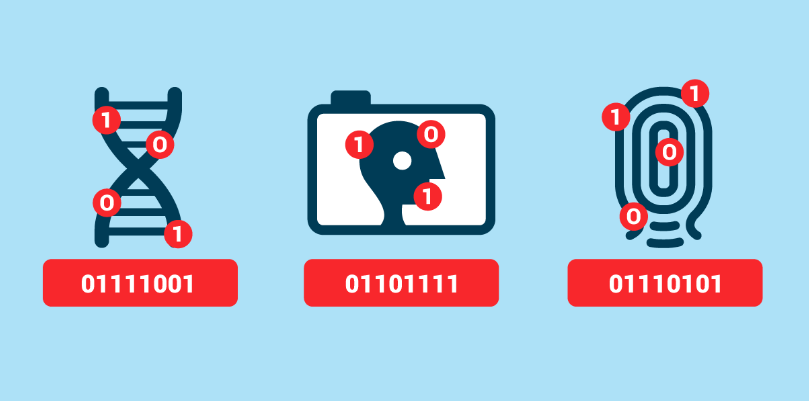
Don’t Fall Victim to Biometric Hacking |
Think your fingerprint or retina scan is unhackable? Think again. Biometric hacking is on the rise, and cybercriminals are getting smarter by the day. Sure, using traits like your face, voice, or fingerprint might feel high-tech and secure—but in reality, they're just another target. |
DNA, facial, and fingerprint data are all susceptible to being hacked. Source: eff.org. |
With threats like database breaches, fake biometrics, and AI-powered deepfakes, your most personal data could be more vulnerable than you think.
|
Tips to Enhance Biometric Security: |
- Enable Multi-Factor Authentication (MFA): Combine biometrics with additional verification like passwords or tokens.
- Secure Biometric Data Storage: Store data locally on devices rather than centralized servers.
-
Regularly Update Systems: Patch software to defend against emerging threats.
- Be Cautious with Personal Information: Avoid sharing photos or recordings that could be used to mimic your identity.
- Educate on Social Engineering Risks: Learn to spot phishing and manipulation
|
Remember: Biometrics offer convenience and stronger access control but still require layered defenses. Staying informed and adopting best practices can help users and organizations protect against evolving biometric threats. |
|
|
|
| Secure Links: The Must-Reads |
|
|
| Secure Links: The Must-Reads |
| |
Phishing Scams Target Netflix Users |
Scammers are sending fake Netflix emails and texts to trick users into giving up personal and financial info. These messages often claim account issues and link to fake login pages. To stay safe, avoid clicking suspicious links and access your account directly through the official Netflix site. |
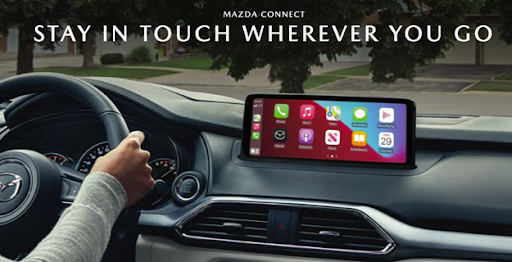
Unpatched Mazda Connect Systems Expose Vehicles to Cyber Threats |
Mazda's infotainment platform, Mazda Connect, harbors unpatched vulnerabilities that could allow hackers to install persistent malware, leaving vehicles susceptible to remote attacks and unauthorized access. These security flaws highlight the growing risks associated with connected car technologies. |
Vehicle owners are urged to stay informed about software updates and implement cybersecurity best practices to safeguard against potential exploits. |
|
|
| Leon Yen is a cybersecurity expert and seasoned tech journalist with over a decade of experience, including founding a cyber risk startup and leading industry-focused research and reporting. |
|
|
|
Liz Ticong is a tech writer specializing in AI and software tools, known for turning complex topics into clear, actionable insights through hands-on testing and analysis. |
|
|
We're looking for talented writers to help shape Cybersecurity Insider. If you're passionate about cyber security, apply to join our team! |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 100, Nashville, TN 37211, USA. |
|
|
|